Security researchers have linked more than 355 domains and subdomains to a network of CyberLeek-themed websites promoting fake Grand Theft Auto VI PC launchers. The sites exploit demand for a Windows version of GTA 6, offering downloads that researchers describe as malicious installers rather than legitimate game software.
The VECERT Foundation published its findings on November 20, 2026, describing infrastructure activity dating back to mid-October. Its investigation of one landing site, cyberleekland[.]com, found a ZIP download offer, misleading software metadata and a script designed to change where visitors obtained the supposed launcher.
The findings come just after GTA VI’s official November 19 release for PlayStation 5 and Xbox Series X|S. Rockstar Games has not listed an official PC edition, making websites promising a Windows launcher particularly suspicious.
The important distinction: VECERT’s count describes related web infrastructure. It does not mean 355 computers were infected, nor does it establish that every identified hostname distributed the same malware.
What Researchers Found in the Fake GTA 6 PC Launcher Network
According to the VECERT Foundation’s original investigation, certificate and domain records revealed a collection of more than 355 domains and subdomains associated with CyberLeek-themed GTA VI download offers.
Researchers reported activity beginning in mid-October 2026, followed by notable increases during November.
The infrastructure included several domain endings, wildcard domain configurations and themed subdomains. Those arrangements can give a download operation additional destinations when a specific page is blocked or becomes unavailable.
But the published count needs careful interpretation.
| Research finding | What it establishes | What it does not establish |
|---|---|---|
| More than 355 domains and subdomains | VECERT identified a substantial CyberLeek-linked web infrastructure set. | It does not establish 355 infections, operators or separate malware samples. |
| Fake Windows launcher website | Researchers examined a page claiming to provide a playable GTA VI PC download. | It does not demonstrate that Rockstar released a PC edition. |
| ZIP archive advertised as installer | The lure offered a compressed file presented as a game launcher. | It does not prove that every visitor downloaded or executed it. |
| Rotating download destinations | Researchers identified JavaScript designed to request changing download links. | It does not identify a specific malware family or confirm individual victims. |
VECERT described the operation as malicious software distribution, but its public report did not include a malware hash list, a verified infection total or a detailed identification of the final executable’s malware family.
How the Fake GTA 6 Launcher Website Tricked Visitors
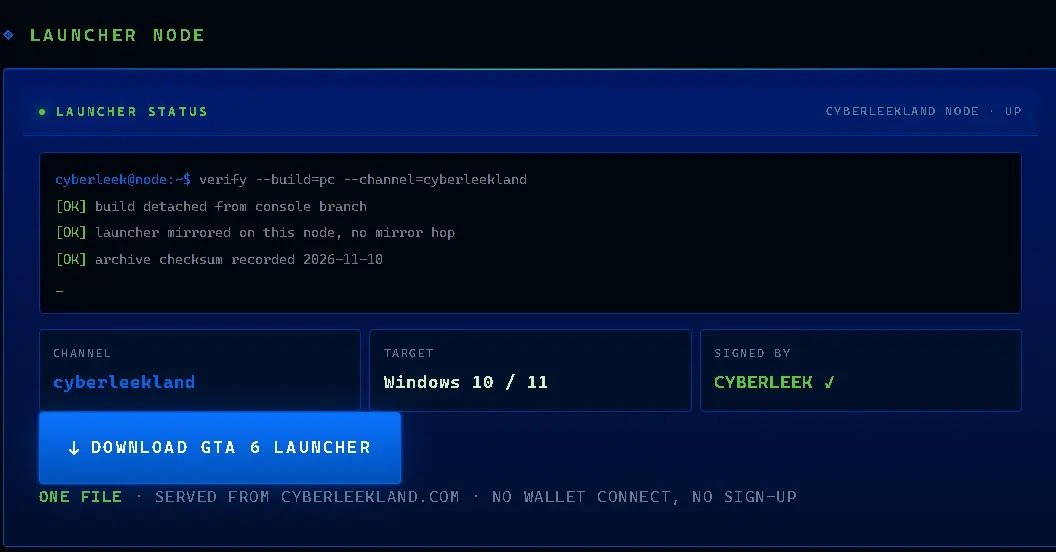
VECERT examined the page structure and a JavaScript file named download.js on one of the reported websites.
The site advertised a supposed playable GTA VI port for Windows 10 and Windows 11, even though no official PC edition had been announced.
Several elements made the offer appear convincing.
1. Search-Friendly Claims About a Nonexistent PC Release
The landing page used terms connected with GTA VI, Windows downloads and the fictional Leonida setting from the game.
Its page metadata and structured data also described the alleged launcher as software. Researchers identified SoftwareApplication and FAQPage markup, alongside a claimed installer path ending in GTA6-Launcher-Setup.exe.
Structured data can help describe a legitimate web page, but it does not authenticate the software being advertised.
A website claiming to offer an official game download can publish that markup without approval from the game’s developer.
2. A ZIP File Presented as a Convenient Download
The page encouraged visitors to obtain a ZIP archive named GTA6Launcher Cyberleek.zip.
It also promoted the download as a simple process without additional advertising barriers.
This presentation matters because users looking for a hard-to-find game build may interpret a direct download as more convenient or credible than a page requesting multiple steps.
However, a ZIP archive is only a container. Its name does not verify the contents, publisher or safety of the executable inside.
3. Download Links That Could Change
Researchers found that the site’s download script contacted a relay endpoint identified as /go?f=json.
According to VECERT’s analysis, the script could obtain changing download destinations on public hosting platforms. A local ZIP archive was available as a fallback when the relay did not respond.
For security teams, this creates a practical detection problem: blocking one file-hosting URL may not address every route offered by the original landing page.
For players, the warning is simpler. A download that moves between unrelated hosting locations is not evidence of an official Rockstar distribution channel.
GTA VI Is Out on Consoles, but There Is No Official PC Release Listed
One reason these lures are convincing is that GTA VI is a real game with exceptionally high public interest.
However, its official release status is important.
Rockstar Games launched Grand Theft Auto VI on November 19, 2026, for PlayStation 5 and Xbox Series X|S.
The company’s official Grand Theft Auto VI website and platform information identify the supported console releases. They do not announce a downloadable Windows PC edition.
That means a website claiming to provide a cracked PC launcher, leaked Windows installer or unofficial early PC version should not be treated as a legitimate game source.
The game’s console launch also changes the wording users should expect from current security warnings. These scams are no longer simply exploiting a game that has not launched; they are exploiting demand for a PC version that Rockstar has not officially released.
Does the 355-Domain Finding Match Earlier GTA VI Scam Research?
The CyberLeek-themed infrastructure was also discussed in an earlier, separate investigation from Netcraft.
In research first published November 3 and updated November 18, 2026, Netcraft identified 121 newly registered domains containing the CyberLeek name during its earlier observation period.
Its researchers emphasized that not all those domains were necessarily fraudulent. Some were fan sites, merchandise pages or other projects.
Among the suspicious examples Netcraft examined, a website impersonating a Rockstar download page offered an executable that multiple security engines identified as a trojan. Another purported launcher required a cryptocurrency payment for activation.
Netcraft also reported that registrations of GTA VI-themed domains more broadly accelerated shortly before the official console launch. Its November 18 update identified at least 800 new registrations during the week before November 17, while cautioning that many were not malicious.
These figures should not be combined into a single campaign total.
The 355+ figure from VECERT includes domains and subdomains associated with its CyberLeek infrastructure investigation. Netcraft’s earlier 121 figure concerns newly registered domains containing a particular name, over a different observation window.
Neither measurement independently establishes how many people were infected or whether a single operator controlled every related site.
Read Netcraft’s original GTA VI scam research and November 18 update for its separate findings.
What Happens If Someone Runs the Fake Launcher?
The immediate danger arises when an untrusted executable is run on a Windows computer.
VECERT warned that installers distributed through these lures could expose a computer to malicious code, including information-stealing malware, loaders or persistent trojans.
Those are potential outcomes described by the researchers. The public report does not establish that every CyberLeek-themed download installed all those malware types or stole a specific set of credentials.
Other investigators have documented different fake GTA VI downloads carrying confirmed malicious payloads. That evidence demonstrates the broader risk but should not be used to assign the same malware to VECERT’s sample without verification.
The distinction between downloading and executing is particularly important.
A ZIP archive appearing in a Downloads folder does not, by itself, prove that an installer was run. A recorded process launch provides a much stronger basis for investigating possible compromise.
What to Do If You Downloaded a Fake GTA 6 PC Installer
If You Downloaded the ZIP but Did Not Run Anything
Do not open or execute the files inside the archive.
Delete the suspicious download and remove any extracted copies. Review browser downloads to identify the source, and do not return to the website to test whether another download works.
Downloading a file alone does not establish an infection, but users who are unsure whether an executable was launched should treat the situation more cautiously.
If You Ran the Installer
Disconnect the affected computer from the network if you suspect malware execution. If it is a workplace-managed device, contact the IT or security team and preserve relevant information about the download and execution.
For a personal Windows PC, open Windows Security → Virus & threat protection and follow Microsoft’s recommended malware-scanning process.
Microsoft also provides an offline scan option that restarts the computer and checks for threats outside the normal Windows environment. Save any open work before starting that procedure.
The official instructions are available in Microsoft’s Windows Security malware-scanning guide.
If investigation indicates that account credentials or browser sessions may have been exposed, use a separate trusted device to change affected passwords, review active sessions and secure associated accounts.
Do not assume deleting the ZIP reverses the effects of an executable that already ran.
For additional prevention steps, see CyberUpdates365’s guide to preventing viruses and malicious code.
Indicators Security Teams Can Investigate
VECERT published examples of infrastructure and file names associated with its analysis. The following indicators are intentionally defanged or presented as non-clickable text.
| Indicator | Reported value | Investigation context |
|---|---|---|
| Examined domain | cyberleekland[.]com | Fake Windows launcher landing page examined by VECERT |
| Related subdomain | api[.]cyberleek[.]link | Example of infrastructure listed in the researcher report |
| Advertised archive | GTA6Launcher Cyberleek.zip | ZIP download name presented by the fake launcher site |
| JavaScript filename | download.js | Script associated with download-link handling |
| Relay path | /go?f=json | Endpoint referenced in download-link rotation |
Security analysts should investigate these values in context. A generic JavaScript filename, ZIP name or URL path is not sufficient on its own to identify a malicious process.
Useful evidence includes a visit to a reported domain followed by an archive download, extraction and an unexpected executable launch.
Organizations can review DNS, web proxy, browser download and endpoint detection logs, where those records are available, to establish what actually happened on a device.
Domain-level indicators may become outdated or change ownership. Blocking known malicious infrastructure is useful, but investigation should not rely on static domain lists alone.
Why This Matters for Everyday PC Gamers
A convincing software page does not need to exploit a technical vulnerability in Windows to put a device at risk. It can instead persuade the user to run software from an unverified source.
The CyberLeek research illustrates three warning signs together: an unannounced PC edition, a compressed installer from an unofficial site and changing download destinations.
Those signals are more important than the page’s visual polish or search-engine visibility.
For broader protection against malicious downloads, impersonation scams and account theft, visit CyberUpdates365’s consumer and small-business cybersecurity defense hub.
Before downloading GTA VI or any other game, check the developer’s official platform and release information. If an unexpected installer has already been executed, investigate the device instead of trusting the file’s name or its claims.
Original Research and Official Guidance
- VECERT Foundation — CyberLeek Infrastructure and Fake GTA VI PC Launcher Investigation, November 20, 2026
- Netcraft — GTA VI Scam and Phishing Research, Updated November 18, 2026
- Rockstar Games — Official Grand Theft Auto VI Release Information
- Rockstar Games Support — GTA VI Platforms and Editions
- Microsoft Support — Virus and Threat Protection in Windows Security