BREAKING NEWS
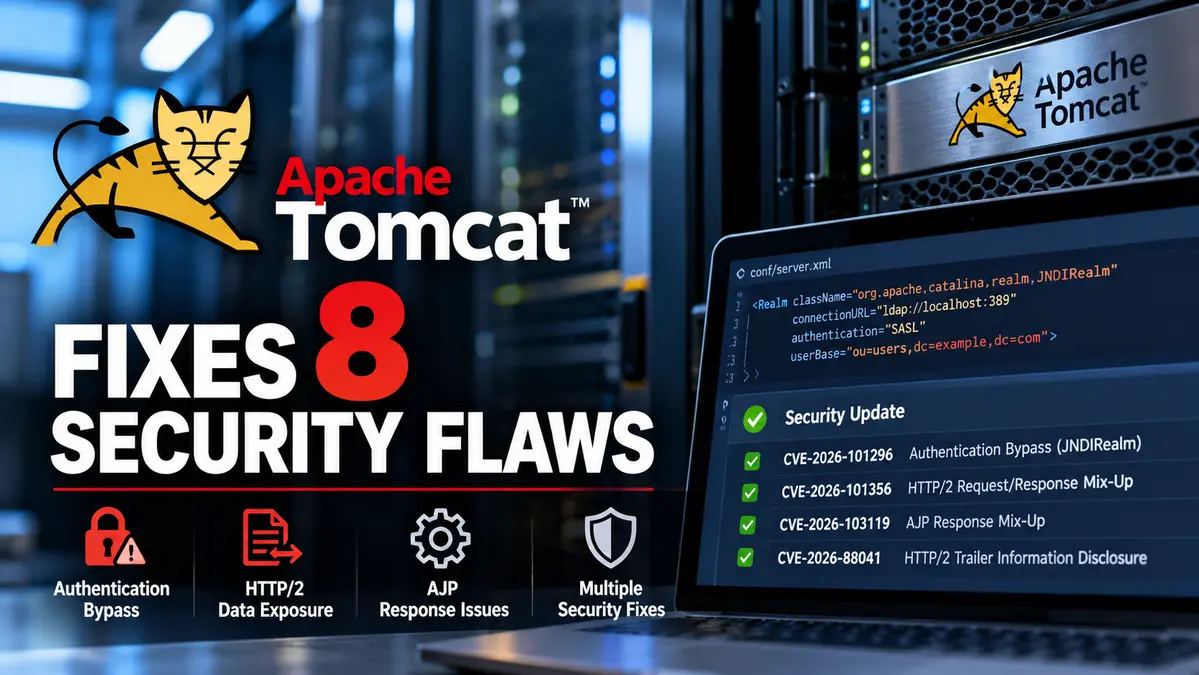
Apache Tomcat Fixes 8 Security Flaws, Including Authentication Bypass
Apache Tomcat has fixed eight vulnerabilities affecting authentication, HTTP/2 processing, AJP responses and several security configurations. Administrators should review the affected versions and upgrade to Tomcat 11.0.27, 10.1.61 or 9.0.123.