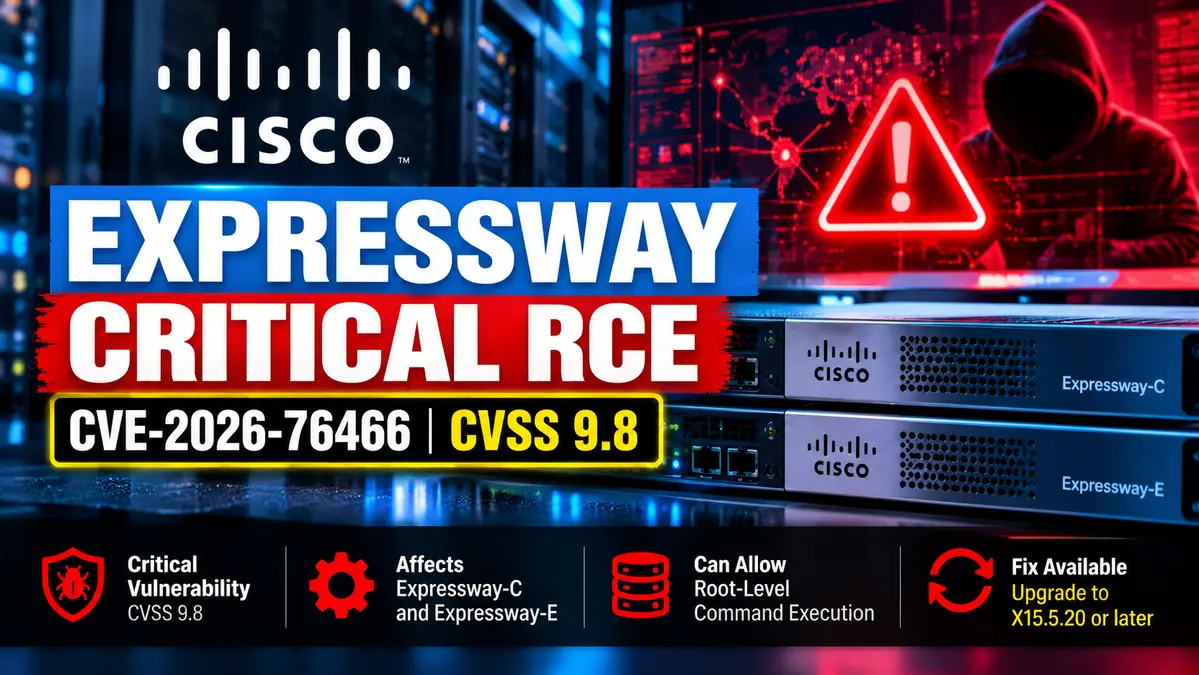
A critical Cisco Expressway RCE vulnerability, tracked as CVE-2026-76466, could allow a remote attacker to execute arbitrary operating-system commands with root privileges on vulnerable clustered Expressway devices.
Cisco disclosed the vulnerability on October 21, 2026, assigning it a CVSS score of 9.8 out of 10. The issue affects the database service used by Cisco Expressway Core and Expressway Edge deployments and involves persistent authentication cookies alongside insufficient client-certificate validation.
An attacker must possess the relevant cookies and have network access to the affected database service. The vulnerability is therefore serious, but it should not be described as allowing every internet user to compromise any Expressway appliance without meeting those conditions.
Cisco has fixed the issue in Expressway X15.5.20 and recommends that organizations running X14 or earlier migrate to a fixed release.
The same October security update also addresses eight additional vulnerability-class CVEs and a separate information-disclosure issue. Cisco says it is not aware of active exploitation of these newly disclosed vulnerabilities.
For related enterprise patch-management and vulnerability-response guidance, explore our CVE Vulnerabilities and Enterprise Security Hub.
Key Findings From Cisco’s Expressway Security Update
- Disclosure date: October 21, 2026.
- Critical vulnerability: CVE-2026-76466, CVSS 9.8.
- Potential impact: Arbitrary operating-system command execution as root.
- Affected products: Cisco Expressway-C and Expressway-E, including virtual and hardware appliance deployments.
- Critical RCE prerequisites: Vulnerable clustered configuration, database-service network access and possession of the relevant persistent cookies.
- Additional fixes: Eight CVE groupings in the security-hardening release and CVE-2026-76435, an information-disclosure flaw.
- First comprehensive fixed release: Cisco Expressway X15.5.20; older X14 releases require migration to a fixed release.
Cisco Expressway RCE CVE-2026-76466: How the Vulnerability Works
Cisco Expressway supports enterprise collaboration and communications environments, including deployments that provide secure connectivity between internal services and remote users.
The product family includes Expressway Core, commonly called Expressway-C, and Expressway Edge, known as Expressway-E.
The critical vulnerability affects a database service feature when Expressway appliances are configured in a cluster.
According to Cisco’s advisory, the underlying problem involves persistent cookies. Additionally, client certificates are not sufficiently validated when the clustering TLS Verify Mode is enabled.
This combination can undermine the expected authentication boundary of the database service.
An attacker who obtains the required cookies and can communicate with the database service may invoke certain remote procedure call operations.
Successful exploitation can allow operating-system commands to run with root privileges on the affected appliance.
Root-level execution is particularly concerning because it provides extensive control over the underlying operating system.
However, Cisco has not disclosed that every remotely reachable Expressway appliance exposes the vulnerable database service to the public internet.
Nor does the advisory establish that an attacker can perform this exploit without obtaining the required cookies.
The vulnerability is classified as CWE-798, concerning the use of hard-coded credentials, and has a CVSS 3.1 base score of 9.8.
Why Cluster Configuration Matters for CVE-2026-76466
The critical RCE has specific deployment requirements.
Cisco identifies Expressway-C and Expressway-E devices running vulnerable releases and configured in a cluster as affected.
Both physical appliances and virtual deployments can be vulnerable when these conditions are met.
A cluster allows multiple Expressway systems to operate together as part of a larger communications infrastructure.
For a clustered service to function securely, communication between members must preserve authentication and trust boundaries.
The reported certificate-validation weakness means that enabling the relevant TLS verification setting does not provide the client-certificate validation expected in the vulnerable implementation.
When this condition is combined with access to persistent cookies, the affected database service may accept unauthorized remote procedure calls.
The distinction matters operationally: a vulnerable software version alone does not establish that every deployment satisfies the prerequisites for this particular RCE.
However, Cisco’s separate Expressway hardening release covers additional vulnerabilities that affect supported devices regardless of configuration.
Administrators should therefore review all relevant advisories, not just the critical RCE configuration requirements.
Which Cisco Expressway Versions Are Vulnerable?
Cisco published the following affected and fixed release information for CVE-2026-76466 and the October hardening release.
| Cisco Expressway Release | Required Action |
|---|---|
| X14 and earlier | Migrate to a supported fixed release. |
| X15.5.3 and earlier | Upgrade to X15.5.20 or a later applicable fixed release. |
| X15.5.20 | First fixed release for CVE-2026-76466 and the October hardening advisory. |
Cisco’s advisories validate the listed affected and fixed versions. Organizations must verify their actual installed release rather than relying on the version recorded in an outdated asset inventory.
The separate information-disclosure vulnerability, CVE-2026-76435, was fixed earlier in X15.5.3.
Nevertheless, administrators updating their systems in response to the full October set should use X15.5.20 or another applicable release confirmed by Cisco to contain all relevant fixes.
Where migration from an older release is required, administrators should check hardware compatibility and vendor-supported upgrade paths.
Cisco Expressway October 2026 Security Hardening Fixes Eight CVE Groups
Cisco also published a broader security-hardening advisory addressing eight CVE identifiers.
The project grouped findings by their underlying Common Weakness Enumeration categories, assigning one CVE to each vulnerability-class grouping.
That means the list should not be interpreted as exactly eight individual underlying software defects.
The published maximum CVSS scores range from 7.8 to 8.6.
| CVE | CVSS | Vulnerability Class |
|---|---|---|
| CVE-2026-76490 | 8.6 | Memory out-of-bounds write category (CWE-787) |
| CVE-2026-76491 | 8.6 | Reachable assertions (CWE-617) |
| CVE-2026-76492 | 8.6 | NULL pointer dereference (CWE-476) |
| CVE-2026-76493 | 8.6 | Uncaught exception (CWE-248) |
| CVE-2026-76494 | 7.8 | Code injection category (CWE-94) |
| CVE-2026-76495 | 7.8 | Improper resource permissions (CWE-732) |
| CVE-2026-76496 | 7.8 | Improper link resolution before file access (CWE-59) |
| CVE-2026-76497 | 7.8 | Insecure temporary-file handling (CWE-377) |
The hardening advisory groups vulnerabilities with different technical causes under one coordinated remediation release.
Some weaknesses concern application availability, such as unhandled exceptions or crashes.
Others relate to memory handling, code generation, file access or permissions.
Cisco does not provide a complete individual exploit chain for every underlying defect in this grouped advisory.
It would therefore be inaccurate to treat every listed issue as a confirmed root-level remote-code-execution path.
CVE-2026-76435: Separate Expressway Information Disclosure Flaw
In addition to the critical RCE and the grouped hardening findings, Cisco disclosed CVE-2026-76435.
This Medium-severity vulnerability has a CVSS score of 5.3.
It involves insufficient authorization checks for HTTP requests during Mobile and Remote Access provisioning.
According to Cisco, an unauthenticated remote attacker may send a crafted URL request and obtain sensitive information that should not be accessible to that requester.
The vulnerability affects Expressway-C and Expressway-E hardware and virtual deployments running vulnerable software.
The official advisory lists X15.5.3 as the first fixed release for the affected X15.5.2-and-earlier range.
Organizations adopting X15.5.20 to address the October critical RCE and hardening issues also move beyond this earlier fixed release.
Information disclosure is distinct from operating-system command execution.
The public advisory does not establish that CVE-2026-76435 independently gives attackers root access.
How AI-Assisted Research Contributed to Cisco’s Expressway Fixes
Cisco says its engineering teams discovered the grouped security-hardening vulnerabilities through internal testing using existing security processes and frontier AI models.
The announcement reflects a broader industry trend toward AI-assisted vulnerability discovery.
Automated analysis can help researchers examine code paths, identify unusual error conditions and surface patterns that require further human review.
However, Cisco does not state that AI independently discovered CVE-2026-76466.
The critical RCE advisory credits Stefan Aleksic of Jane Street with reporting that vulnerability.
The separate information-disclosure issue was identified during the resolution of a Cisco Technical Assistance Center support case.
These findings have different discovery histories and should not be grouped under a universal claim that AI found every October Expressway flaw.
Is CVE-2026-76466 Being Actively Exploited?
As of Cisco’s October 21 advisory, the company’s Product Security Incident Response Team was not aware of public announcements or malicious exploitation involving CVE-2026-76466.
Cisco similarly reported no known malicious exploitation of the hardening CVEs or the separate information-disclosure flaw.
That does not mean the vulnerabilities are safe to leave unpatched.
A CVSS 9.8 flaw capable of executing commands as root creates serious potential consequences when the required conditions are present.
Administrators should prioritize exposed and clustered environments while distinguishing possible exploitation from confirmed attacks.
Security investigations should focus on actual abnormal behavior, verified evidence and the affected product configuration rather than assuming every older Expressway appliance has already been compromised.
How Administrators Can Identify Vulnerable Cisco Expressway Deployments
Organizations should begin with a verified inventory of all Expressway-C and Expressway-E installations.
1. Identify Device Roles and Deployment Types
Record whether each Expressway system operates as a Core or Edge device and whether it is a virtual or hardware appliance.
Include production, staging, disaster recovery and geographically distributed instances.
2. Verify the Installed Software Release
Use the product’s supported administrative interface to view its running software version.
Compare the reported release with the official Cisco fixed-version table.
For older X14 deployments, follow the vendor-supported migration path to a fixed release.
3. Review Cluster Membership
Determine which Expressway systems operate in a cluster.
Cluster membership is particularly important when assessing CVE-2026-76466.
Record the configuration and network boundaries associated with cluster communication.
4. Check Database-Service Network Exposure
Review network rules governing communication with the Expressway database service.
Only authorized, required systems should be able to reach sensitive management and inter-node interfaces.
Reducing unnecessary access can lower exposure while an upgrade is prepared, but Cisco states that no workaround fully addresses the vulnerabilities.
5. Review Authentication and Administrative Activity
Inspect available audit logs for unexplained administrative sessions, unauthorized configuration changes and unusual inter-node communication.
Because the public advisory does not provide incident-specific detection signatures, these checks are investigative measures rather than definitive indicators of CVE-2026-76466 exploitation.
Cisco Expressway RCE: Official Patch and Mitigation Guidance
Cisco has released software updates that address the critical RCE and the hardening vulnerabilities.
The company states that no workarounds fully address the disclosed issues.
Organizations should install X15.5.20 or another applicable fixed release supported for their deployment.
Before upgrading, administrators should:
- Identify installed releases and cluster configurations.
- Confirm hardware and virtual appliance compatibility.
- Review Cisco-supported upgrade and migration paths.
- Prepare configuration backups through supported administrative tools.
- Coordinate maintenance with communications and network teams.
- Assess the impact of planned restarts on remote access and call-related workflows.
- Verify access to the required software through Cisco support or approved distribution channels.
Do not assume a release can be installed directly from any older version without intermediate steps.
Cisco advises customers to verify memory capacity, software compatibility and supported configurations before upgrading.
Where the upgrade path is unclear, contact Cisco Technical Assistance Center or an authorized support provider.
Post-Upgrade Verification Checklist
After installing the security release, verify that the production environment is running the intended fixed software.
- Version: Confirm the actual running release on every Expressway-C and Expressway-E node.
- Cluster: Verify intended members are healthy and communicating correctly.
- Certificates: Validate certificate trust and expected secure inter-node communication.
- Remote access: Test approved Mobile and Remote Access workflows.
- Service health: Confirm normal communications functionality and required integrations.
- Exposure: Review access to management and database-related interfaces.
- Logging: Check system warnings and unexpected administrative activity.
- Inventory: Update asset records with the deployed version and verification evidence.
A completed upgrade closes the documented vulnerability in the updated software, but it does not automatically prove that the system was never accessed without authorization.
If credible signs of compromise exist, investigate affected devices and associated credentials through a formal incident-response process.
Confirmed vs Unknown: Cisco Expressway October 2026 Advisories
Confirmed
- Cisco disclosed CVE-2026-76466 on October 21, 2026.
- The vulnerability has a CVSS 3.1 score of 9.8.
- A successful exploit could execute commands as root.
- The critical vulnerability affects vulnerable Expressway devices configured in a cluster.
- Attackers must possess the required cookies and reach the relevant database service.
- X15.5.20 contains the critical RCE and grouped hardening fixes.
- The hardening advisory lists eight CWE-based CVE groupings.
- CVE-2026-76435 is a separate Medium-severity information-disclosure vulnerability.
- Cisco reports no known malicious exploitation of the disclosed Expressway issues.
Unknown or Not Established
- A confirmed number of compromised organizations.
- Publicly verified attacks exploiting CVE-2026-76466.
- That every Expressway installation is susceptible to the critical RCE regardless of configuration.
- That attackers can exploit the critical flaw without the necessary cookies.
- A universal exploit chain for all hardening-related CVE groupings.
- Whether affected organizations have completed patching.
CyberUpdates365 Analysis
The Cisco Expressway security update illustrates why the real impact of a critical vulnerability depends on both the affected software and its deployment configuration.
CVE-2026-76466 has a CVSS score of 9.8 and can lead to root-level command execution.
Those consequences are severe, but an accurate risk assessment must also consider the documented cookie requirement, network reachability and cluster configuration.
Organizations that focus only on the severity score may overlook the technical prerequisites that determine which devices require the fastest response.
At the same time, operators should not dismiss other Expressway vulnerabilities because a particular deployment does not satisfy the conditions for the critical RCE.
The broader hardening advisory includes weaknesses affecting both Expressway-C and Expressway-E regardless of configuration.
This makes comprehensive version management more effective than trying to evaluate the critical vulnerability in isolation.
The incident also highlights the importance of securing trust relationships between infrastructure components.
Cluster communications often depend on authentication material and certificate verification to separate trusted nodes from unauthorized systems.
If those mechanisms fail, services intended primarily for internal coordination can become a serious attack surface.
For security teams, the practical priorities are clear: maintain accurate appliance inventories, verify cluster exposure, protect administrative and inter-node communication, and apply the vendor’s fixed release.
The wider lesson is that network infrastructure security requires both correct software patching and reliable protection of the relationships between trusted systems.
Research Evidence
- Vendor: Cisco.
- Disclosure date: October 21, 2026.
- Critical CVE: CVE-2026-76466.
- CVSS score: 9.8 Critical.
- Potential impact: Root-level operating-system command execution.
- Affected products: Cisco Expressway-C and Expressway-E.
- Critical RCE configuration: Vulnerable clustered deployment.
- Additional prerequisites: Required cookies and database-service network access.
- Fixed release: X15.5.20.
- Older release guidance: X14 and earlier must migrate to a fixed release.
- Additional hardening CVEs: CVE-2026-76490 through CVE-2026-76497.
- Additional information-disclosure CVE: CVE-2026-76435, CVSS 5.3.
- Confirmed exploitation: Not known to Cisco PSIRT at disclosure.
- Workarounds: None that fully address the disclosed issues.
Frequently Asked Questions
What is CVE-2026-76466?
CVE-2026-76466 is a critical Cisco Expressway database-service vulnerability that can allow a remote attacker meeting specific prerequisites to execute commands with root privileges.
What is the CVSS score of Cisco Expressway RCE?
Cisco assigns CVE-2026-76466 a CVSS 3.1 base score of 9.8, rated Critical.
Does the vulnerability affect every Expressway server?
The critical RCE specifically affects vulnerable Expressway-C and Expressway-E systems configured in a cluster. Other vulnerabilities in the hardening release have different affected conditions.
Does the attacker need credentials?
Cisco describes an unauthenticated attacker, but successful exploitation requires possession of the relevant persistent cookies and network access to the database service.
Which Cisco Expressway version fixes CVE-2026-76466?
Cisco identifies X15.5.20 as the first fixed release for vulnerable X15.5.3-and-earlier systems. X14 and earlier deployments must migrate to a fixed release.
Are the Cisco Expressway vulnerabilities being actively exploited?
Cisco PSIRT said it was not aware of malicious exploitation of the disclosed Expressway vulnerabilities at the time of its October 21 advisories.
Are there workarounds?
Cisco says no workarounds fully address the vulnerabilities. Restricting unnecessary network access may reduce exposure but is not a substitute for upgrading.
What other vulnerabilities were patched?
The coordinated Expressway release covers eight additional CVE groupings in a security-hardening update and CVE-2026-76435, a separate information-disclosure flaw.
Final Takeaway
Cisco’s October 2026 Expressway security release addresses a critical root-level remote-code-execution vulnerability alongside multiple additional hardening and information-disclosure issues.
The most severe finding, CVE-2026-76466, carries a CVSS score of 9.8 and affects vulnerable clustered Expressway systems under specific conditions.
Organizations should verify installed versions, review cluster communication exposure and upgrade to Cisco Expressway X15.5.20 or another vendor-confirmed fixed release.
The priority is to patch the affected infrastructure while preserving the distinction between a critical potential outcome and confirmed real-world exploitation.
Could another enterprise access appliance expose your network to remote code execution?
Cisco’s Expressway flaw affects a specific clustered configuration. Our separate F5 BIG-IP investigation examines a different access-management vulnerability with documented exploitation and configuration-specific exposure.
Read: F5 BIG-IP APM Zero-Day CVE-2026-94127 Actively Exploited for RCE →