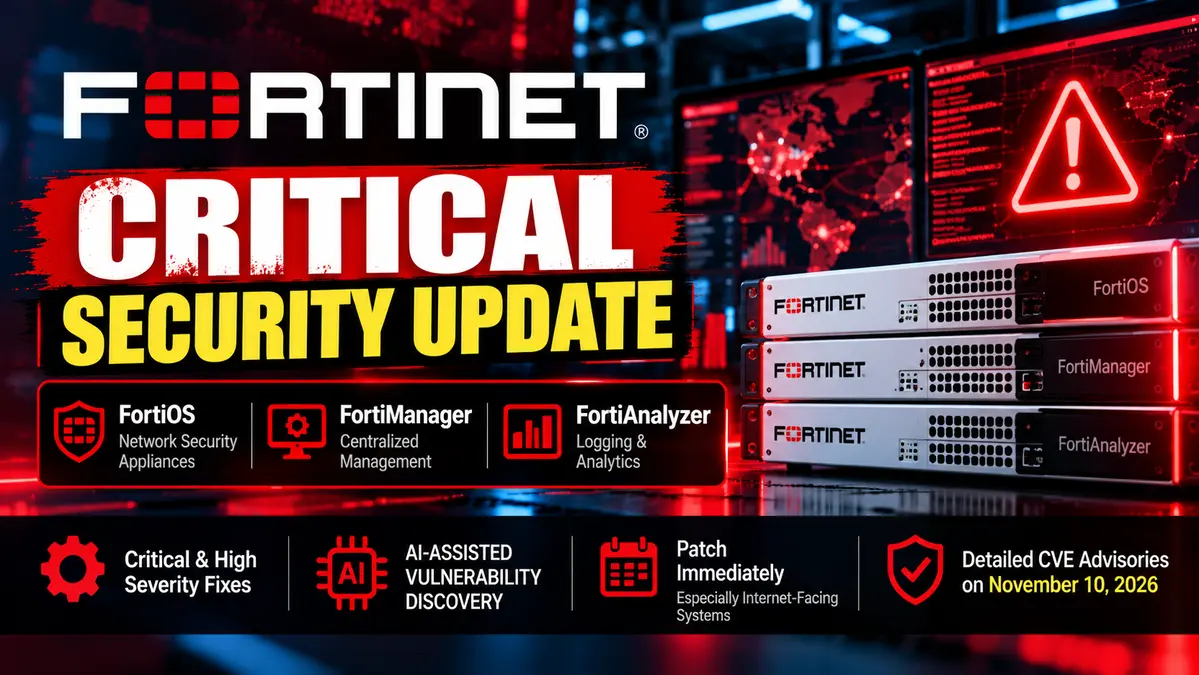
A Fortinet security update announced for October 22, 2026, delivers critical and high-severity fixes for FortiOS, FortiManager and FortiAnalyzer, with the company urging customers to patch internet-facing systems without delay.
Fortinet Chief Information Security Officer Carl Windsor warned that artificial intelligence is accelerating vulnerability discovery and potentially shortening exploit-development timelines. The company also confirmed that AI-assisted testing helped its own researchers identify security weaknesses addressed in the coordinated updates.
The release follows related security updates for FortiMail and FortiAuthenticator, extending Fortinet’s October security response across five major product families.
Fortinet published affected version ranges and required upgrades, but detailed public PSIRT advisories for the coordinated release are scheduled for November 10, 2026.
That means administrators can identify and update affected devices now, even though complete technical descriptions and individual CVE details have not yet been published.
For broader guidance on enterprise security vulnerabilities and remediation, explore our CVE Vulnerabilities and Enterprise Security Hub.
Key Findings From Fortinet’s October 2026 Security Update
- Announcement date: October 21, 2026.
- Coordinated security release: October 22, 2026.
- Main affected products: FortiOS, FortiManager and FortiAnalyzer.
- Additional products: FortiMail and FortiAuthenticator, with related October security updates.
- Severity: Critical and High, according to Fortinet.
- Immediate priority: Internet-facing appliances and exposed management interfaces.
- Detailed PSIRT advisories: Scheduled for November 10, 2026.
Fortinet Security Update: Why the October Release Is Urgent
Fortinet’s coordinated security release covers technologies that organizations rely on to protect and manage enterprise networks.
FortiOS powers Fortinet network security appliances, including FortiGate firewalls. FortiManager provides centralized management of security devices, while FortiAnalyzer handles security logging, reporting and analytics.
Because these products operate close to critical network boundaries, vulnerabilities in their management or processing components can create serious security exposure.
Fortinet describes the October fixes as addressing Critical and High-severity security weaknesses.
The company has not yet published a complete public list of individual CVEs for the coordinated FortiOS, FortiManager and FortiAnalyzer release.
Therefore, the available announcement does not establish that every affected product contains an unauthenticated remote-code-execution vulnerability or that every exposed installation can be compromised through the same technique.
Nevertheless, Fortinet is urging customers to treat these updates as a priority, especially when devices are accessible from untrusted networks.
Administrators should identify deployed products, check their installed firmware versions and follow the vendor’s supported upgrade paths.
FortiOS Critical Vulnerabilities: Affected and Fixed Versions
FortiOS is the operating system used by Fortinet network security appliances.
Fortinet’s October announcement identifies four affected FortiOS release branches and their corresponding fixed versions.
| FortiOS Branch | Affected Versions | Fixed Version |
|---|---|---|
| 8.0 | 8.0.0–8.0.1 | 8.0.2 or later |
| 7.6 | 7.6.0–7.6.7 | 7.6.8 or later |
| 7.4 | 7.4.0–7.4.12 | 7.4.13 or later |
| 7.2 | 7.2.0–7.2.13 | 7.2.14 or later |
These are the minimum fixed releases identified in Fortinet’s coordinated update announcement.
Before deploying firmware, administrators should check the vendor-supported upgrade path for their exact appliance model and currently installed version.
The correct upgrade sequence may depend on firmware compatibility, high-availability configuration and supported intermediate releases.
Organizations should not assume that installing a newer firmware image without reviewing the supported upgrade path is always safe.
FortiManager and FortiAnalyzer Security Fixes
FortiManager and FortiAnalyzer also require updates under Fortinet’s coordinated security release.
Although some branch numbers are shared with FortiOS, their minimum fixed versions differ.
| Product | Branch | Affected Versions | Fixed Version |
|---|---|---|---|
| FortiManager | 8.0 | 8.0.0–8.0.1 | 8.0.2+ |
| FortiManager | 7.6 | 7.6.0–7.6.7 | 7.6.8+ |
| FortiManager | 7.4 | 7.4.0–7.4.11 | 7.4.12+ |
| FortiManager | 7.2 | 7.2.0–7.2.12 | 7.2.13+ |
| FortiAnalyzer | 8.0 | 8.0.0–8.0.1 | 8.0.2+ |
| FortiAnalyzer | 7.6 | 7.6.0–7.6.7 | 7.6.8+ |
| FortiAnalyzer | 7.4 | 7.4.0–7.4.11 | 7.4.12+ |
| FortiAnalyzer | 7.2 | 7.2.0–7.2.12 | 7.2.13+ |
FortiManager requires particular attention because it can manage numerous network security appliances from a centralized interface.
FortiAnalyzer should also be included in the security inventory because its logging and analytics capabilities can support operational monitoring and incident investigations.
The initial Fortinet announcement does not establish a universal exploitation mechanism affecting all three product families.
FortiMail and FortiAuthenticator Security Updates
Fortinet’s October security announcement also references updates for FortiMail and FortiAuthenticator.
These products perform different security functions and have their own affected version ranges.
| Product | Affected Versions | Required Fix |
|---|---|---|
| FortiMail 8.0 | 8.0.0–8.0.1 | 8.0.2+ |
| FortiMail 7.6 | 7.6.0–7.6.6 | 7.6.7+ |
| FortiMail 7.4 | 7.4.0–7.4.8 | 7.4.9+ |
| FortiMail 7.2 | 7.2.0–7.2.9 | Move to a supported 7.4 or later branch according to vendor guidance |
| FortiAuthenticator 8.0 | 8.0.0–8.0.3 | 8.0.4+ |
| FortiAuthenticator 6.6 | 6.6.0–6.6.10 | 6.6.11+ |
FortiMail protects email infrastructure, while FortiAuthenticator supports identity verification and authentication services.
Organizations operating these products should review the applicable security advisories and product-specific upgrade requirements rather than treating the coordinated release as a single firmware package.
Fortinet has also faced active exploitation of a separate FortiMail vulnerability, CVE-2026-104286. Our earlier investigation explains the actively exploited FortiMail zero-day CVE-2026-104286, including its attack conditions, affected versions and remediation guidance.
That earlier incident is separate from the newly disclosed coordinated Fortinet updates. Confirmed exploitation of the FortiMail zero-day does not establish that the undisclosed FortiOS, FortiManager or FortiAnalyzer flaws are also being actively exploited.
Why Fortinet Is Warning About AI-Assisted Exploit Development
Fortinet says advanced AI models are changing how security researchers discover vulnerabilities and how attackers may approach exploit development.
The company reports using frontier AI-assisted testing to examine software code paths, protocol handling and configuration logic.
Fortinet also describes collaboration with organizations including Anthropic, OpenAI, Google and SpaceX as part of its security-testing efforts.
The company warns that attackers may use similar technologies to examine security patches and identify weaknesses in unpatched systems.
One technique relevant to this concern is patch diffing.
Patch diffing involves comparing older and newer software versions to identify code changes introduced by a security update.
Researchers can use those differences to understand how a vulnerability was corrected.
Attackers may also analyze those changes to identify the vulnerable behavior in systems that have not yet been upgraded.
Fortinet warns that AI-assisted analysis could reduce the time needed to develop working exploits from weeks to hours or days.
This is a vendor assessment of emerging risks, not evidence that attackers have already weaponized every vulnerability addressed in the coordinated release.
For defenders, the main implication is that available security patches should be prioritized before detailed exploitation information becomes widely available.
Why Fortinet Is Delaying Detailed CVE Disclosure Until November 10
Fortinet plans to publish full public PSIRT advisories for these coordinated updates on November 10, 2026.
According to the company’s announcement, the disclosure schedule is intended to balance transparency with customer security.
Publishing fixed firmware before complete vulnerability details gives customers an opportunity to deploy updates ahead of broader technical disclosure.
However, delayed disclosure does not mean that the underlying vulnerabilities are low risk.
Fortinet explicitly describes the coordinated release as containing Critical and High-severity security fixes.
Organizations should therefore not wait for CVE identifiers or public proof-of-concept material before beginning remediation.
Once the detailed PSIRT advisories become public, administrators should review them against their installed versions and confirm that the intended vulnerabilities were addressed.
The initial announcement does not justify assigning unannounced CVE identifiers, numerical CVSS scores or specific attack paths to the newly fixed FortiOS, FortiManager and FortiAnalyzer issues.
Are the New Fortinet Vulnerabilities Being Actively Exploited?
Fortinet’s October coordinated-update announcement does not confirm active exploitation of the newly undisclosed vulnerabilities.
This distinction is particularly important because earlier Fortinet vulnerabilities, including the separate FortiMail CVE-2026-104286, have been associated with confirmed attacks.
Evidence of exploitation involving one product or CVE cannot automatically be applied to a different security release.
Nevertheless, vulnerabilities affecting internet-facing security appliances deserve urgent attention.
These devices can occupy privileged positions in enterprise networks and may provide access to administrative functions, remote connectivity and security controls.
Security teams should monitor for unexpected administrator logins, unfamiliar privileged accounts, suspicious configuration changes and unusual network activity.
Such events may justify an investigation, but they are not specific indicators of the October coordinated vulnerabilities.
How to Identify Fortinet Devices That Need Patching
Organizations should begin by building an accurate inventory of deployed Fortinet products.
1. Inventory Network Security Appliances
Include FortiGate firewalls, FortiManager, FortiAnalyzer, FortiMail and FortiAuthenticator systems.
Review physical appliances, virtual appliances, cloud deployments, disaster recovery systems and devices managed by third parties.
2. Check FortiOS Firmware Versions
Administrators with authorized FortiOS CLI access can check the installed firmware version using:
get system statusCompare the reported version with the relevant fixed version published by Fortinet.
For other Fortinet products, use the supported administrative interface or product-specific version commands.
3. Identify Exposed Management Interfaces
Determine whether HTTPS or SSH administrative interfaces are accessible from untrusted networks.
Review trusted-host restrictions, interface configuration and administrative access rules.
Internet-facing management services should receive particular attention during patch prioritization.
4. Review Cloud-Managed Deployments
Fortinet says FortiSASE updates are handled automatically ahead of the coordinated release.
FortiManager Cloud and public-cloud deployments may follow different update procedures.
Administrators should verify the actual service state instead of assuming every cloud-managed product receives updates in the same way.
Fortinet’s Recommended Emergency Mitigations
Organizations that cannot immediately deploy the fixed firmware should reduce exposure while preparing the required updates.
Temporary mitigations can help limit attack opportunities, but they do not replace the official security patches.
Restrict Administrative Access
Limit administrative HTTPS and SSH access to trusted management addresses.
Where practical, remove administrative interfaces from direct public internet exposure.
Fortinet specifically recommends preventing public internet access to FortiManager administrative interfaces.
Use Protected Management Channels
Where suitable, administer security appliances through a protected management network, VPN or SASE service.
This can reduce the number of untrusted systems able to reach privileged management interfaces.
Secure Administrator Accounts
Use strong, unique credentials and enforce multifactor authentication where supported.
Review privileged accounts and remove access that is no longer necessary.
Apply Appropriate Compensating Controls
Fortinet also discusses virtual patching as a temporary option.
Compensating controls should be assessed against the actual product, vulnerable interface and deployment architecture.
Because detailed technical advisories have not yet been published, administrators should not assume that one generic security rule blocks every issue in the coordinated update.
How to Apply the October Fortinet Security Updates Safely
Fortinet recommends preparing maintenance windows for October 22 and 23, particularly for internet-facing infrastructure.
Before installing firmware, administrators should review the supported upgrade path and create appropriate configuration backups.
A practical enterprise patching process includes:
- Confirming device model and current firmware version.
- Identifying the correct minimum fixed release.
- Checking product-specific upgrade paths and compatibility requirements.
- Preparing verified configuration backups.
- Reviewing high-availability cluster dependencies.
- Scheduling changes with network and application owners.
- Installing the appropriate firmware through supported Fortinet procedures.
- Confirming successful restart and cluster synchronization.
- Testing essential network and management functions.
- Monitoring logs and security events after deployment.
High-availability deployments require particular care because firmware changes can affect failover behavior and service availability.
Administrators should follow Fortinet’s documented upgrade procedures instead of applying an assumed universal sequence to every product.
Where a device cannot run the identified fixed release, contact Fortinet support to determine the appropriate supported remediation path.
Patch Verification Checklist for Fortinet Administrators
After maintenance, verify that affected devices are actually running the required fixed firmware.
- Firmware version: Confirm the running build meets the appropriate fixed-version requirement.
- Administrative access: Verify HTTPS and SSH management exposure matches approved policy.
- Accounts: Review administrator accounts, trusted hosts and MFA settings.
- Security policies: Confirm expected firewall and security rules remain active.
- Remote access: Test legitimate VPN and other remote connectivity services.
- High availability: Validate cluster state, synchronization and failover readiness.
- Central management: Confirm FortiManager connectivity to managed devices.
- Logging: Verify FortiAnalyzer continues receiving expected events.
- Audit evidence: Review suspicious administrative or configuration changes.
- Inventory: Record completed firmware updates and verification results.
A successful firmware installation does not automatically establish that a previously compromised device is clean.
If unauthorized access is suspected, investigate credentials, administrator accounts, persistence mechanisms and related infrastructure separately.
Confirmed vs Unknown: Fortinet October 2026 Security Update
Confirmed
- Fortinet announced coordinated security updates on October 21, 2026.
- FortiOS, FortiManager and FortiAnalyzer security releases were scheduled for October 22.
- The updates include Critical and High-severity fixes.
- Related October security updates cover FortiMail and FortiAuthenticator.
- Fortinet published affected version ranges and minimum fixed releases.
- Some vulnerabilities were identified through AI-assisted security testing.
- Fortinet recommends prioritizing internet-facing appliances.
- Detailed public PSIRT advisories are planned for November 10.
Unknown or Not Established
- The complete public CVE list for the coordinated FortiOS, FortiManager and FortiAnalyzer updates.
- Individual CVSS scores and exploitation prerequisites.
- Confirmed active exploitation of the newly undisclosed vulnerabilities.
- The number of organizations affected by each issue.
- A verified threat actor exploiting the new fixes.
- A universal remote-code-execution path across every listed product.
- Whether all customer deployments have completed patching.
CyberUpdates365 Analysis
Fortinet’s coordinated October security release highlights an increasingly important challenge for enterprise defenders: critical infrastructure may need patching before full public vulnerability descriptions become available.
Security teams must therefore rely on authoritative vendor guidance, accurate asset inventories and the real exposure of their deployed devices.
Network security appliances can provide firewall enforcement, remote access, centralized management and security telemetry.
An upgrade failure or configuration change may affect business-critical connectivity.
However, delaying a critical security update may leave exposed systems at risk for longer.
Fortinet’s warning about AI-assisted patch analysis adds urgency to this decision.
If attackers can identify vulnerable behavior more quickly by analyzing software changes, the available remediation window may shrink.
That possibility does not establish that exploits already exist for each newly patched vulnerability.
The immediate operational challenge is knowing exactly which products and branches require upgrades.
For example, FortiOS 7.4 and FortiManager 7.4 have different minimum fixed versions under this coordinated release.
Administrators who check only the branch number could incorrectly conclude that every device is protected.
Effective remediation should connect asset inventory, approved upgrade paths, configuration backups, deployment validation and post-upgrade monitoring.
Organizations should also distinguish between this coordinated release and earlier Fortinet incidents with documented exploitation.
The central lesson is that network security depends on verified firmware, controlled administrative exposure and disciplined patch deployment—not simply the availability of an update.
Research Evidence
- Vendor: Fortinet.
- Announcement: October 21, 2026.
- Coordinated security release: October 22, 2026.
- Primary affected products: FortiOS, FortiManager and FortiAnalyzer.
- Additional product updates: FortiMail and FortiAuthenticator.
- Severity: Critical and High, as described by Fortinet.
- FortiOS 7.4 minimum fixed version: 7.4.13.
- FortiManager 7.4 minimum fixed version: 7.4.12.
- FortiAnalyzer 7.4 minimum fixed version: 7.4.12.
- AI-assisted testing: Reported by Fortinet.
- Detailed PSIRT publication: Planned for November 10, 2026.
- Active exploitation of newly undisclosed coordinated flaws: Not established in the announcement.
- Primary remediation: Install the appropriate fixed firmware and verify deployment.
Frequently Asked Questions
What is included in the October 2026 Fortinet security update?
The coordinated release includes Critical and High-severity fixes for FortiOS, FortiManager and FortiAnalyzer, following related updates for FortiMail and FortiAuthenticator.
Which FortiOS versions require upgrading?
Fortinet identifies affected versions in the 8.0, 7.6, 7.4 and 7.2 branches. The minimum fixed builds are 8.0.2, 7.6.8, 7.4.13 and 7.2.14, respectively.
Which FortiManager and FortiAnalyzer versions are fixed?
The corresponding minimum fixed releases are 8.0.2, 7.6.8, 7.4.12 and 7.2.13 for the relevant branches.
Are the newly disclosed Fortinet flaws actively exploited?
The October coordinated-update announcement does not establish active exploitation of the newly undisclosed vulnerabilities. Earlier Fortinet incidents involving confirmed attacks are separate.
Why are detailed CVE advisories scheduled for November 10?
Fortinet says the disclosure schedule is intended to give customers time to deploy fixes while balancing transparency with security risks.
Did AI help identify these vulnerabilities?
Fortinet reports using advanced AI-assisted testing as part of its vulnerability-discovery process, alongside human security research.
What should administrators do if immediate patching is impossible?
Restrict exposed management interfaces, use protected administrative channels, enforce strong credentials and MFA, and apply appropriate temporary mitigations. These steps do not replace installing fixed firmware.
How can organizations verify successful Fortinet patching?
Check the running firmware version against the correct product-specific fixed release and validate administrative access, security policies, logging, connectivity and high-availability health.
Final Takeaway
Fortinet’s October 2026 security updates cover multiple enterprise network security products, including FortiOS, FortiManager, FortiAnalyzer, FortiMail and FortiAuthenticator.
The company confirms Critical and High-severity fixes and recommends prioritizing exposed systems without waiting for complete technical CVE disclosures.
Administrators should review affected version ranges, install the appropriate fixed builds and verify the security and functionality of updated appliances.
The safest approach is to treat the coordinated release as a network security maintenance priority while keeping confirmed findings separate from unverified exploitation claims.
Are your Fortinet appliances protected against actively exploited vulnerabilities?
Fortinet’s latest security updates span several products. Our earlier investigation covers a separate FortiMail zero-day with confirmed exploitation, affected versions and practical remediation guidance.
Read: FortiMail Zero-Day CVE-2026-104286 Actively Exploited in Attacks →