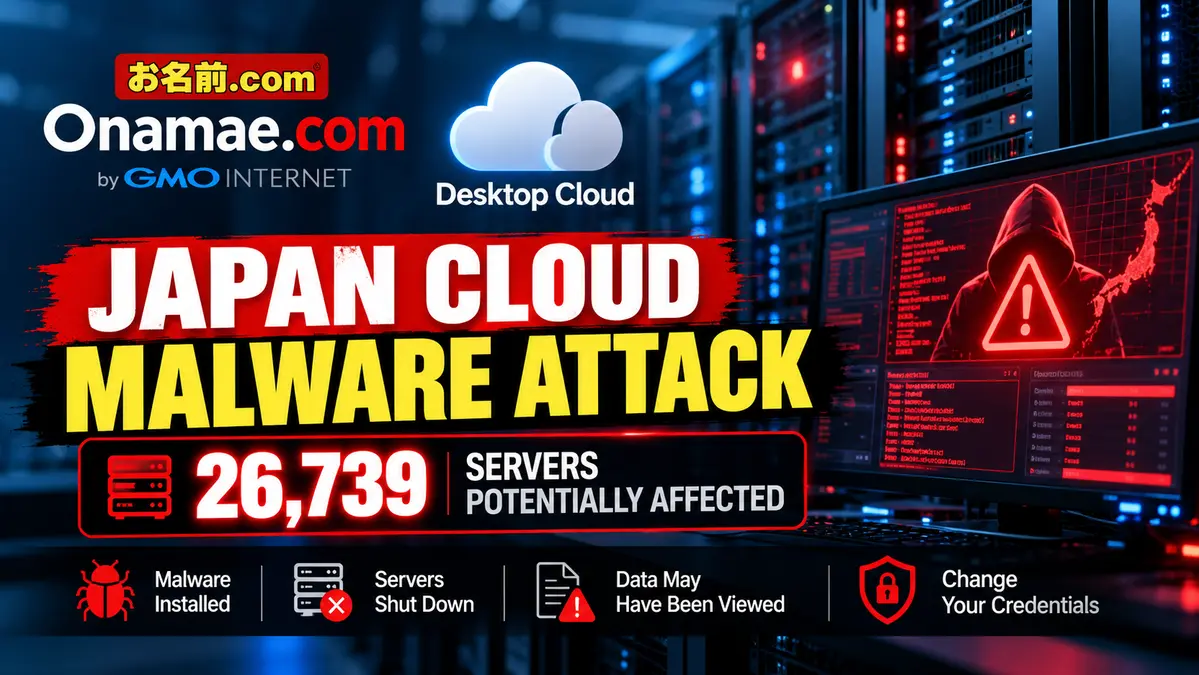
An Onamae Cloud malware attack forced Japanese hosting provider GMO Internet to suspend its Desktop Cloud service after unauthorized access led to malicious programs being installed on some customer servers.
The company confirmed the intrusion on October 20, 2026, and identified 26,739 servers as potentially affected. Beginning at 4:00 a.m. Japan time on October 21, it started shutting down customer servers across all Onamae.com Desktop Cloud plans to prevent additional damage.
GMO Internet also warned that information stored on affected servers may have been viewed by an unauthorized party. It urged customers to change passwords and other authentication credentials stored or used in their cloud environments.
The distinction between possible exposure and confirmed theft is important. The company has not confirmed misuse of customer information, and the 26,739 figure represents potentially affected servers rather than a verified count of malware infections.
The initial entry point, malware family, attacker identity and full scope of the intrusion remain under investigation.
For a wider explanation of confirmed incidents, potential data exposure and breach response, see our Data Breach Coverage and Response Guide.
Key Findings From the Onamae Desktop Cloud Breach
- Provider: Onamae.com Desktop Cloud, operated by GMO Internet.
- Intrusion confirmed: October 20, 2026.
- Potentially affected servers: 26,739.
- Confirmed malicious activity: Unauthorized programs installed in some customer server environments.
- Customer data risk: Information stored on servers may have been viewed.
- Service disruption: All Desktop Cloud plans affected by the shutdown.
- Customer action: Change potentially exposed passwords, investigate accounts and watch for phishing.
Onamae Cloud Malware Attack: What Happened?
Onamae.com is a Japanese internet services brand operated by GMO Internet, offering domain registration and various hosting products.
Its Desktop Cloud service provides remotely accessible cloud server environments that customers can use to keep applications running without relying on their own computers.
On October 20, GMO Internet confirmed that an unauthorized third party had accessed the Desktop Cloud environment and installed malicious programs in some customer server systems.
On October 21, the provider issued a public incident notification explaining that the compromise could have exposed information stored inside affected servers.
To limit additional damage while investigating, the company began progressively shutting down customer servers at 4:00 a.m. Japan Standard Time on October 21.
All Desktop Cloud service plans were included in that suspension.
At the time of the notice, GMO had not provided a confirmed date for restoring the service.
The provider said additional information would be released as its investigation progressed.
The official announcement does not establish that an attacker gained access to every Onamae.com product or compromised the company’s entire infrastructure portfolio.
Were 26,739 Onamae Servers Infected With Malware?
No verified public evidence establishes that all 26,739 servers were infected.
GMO Internet identifies the figure as the number of server environments that may have been affected by the incident.
The company separately confirms that unauthorized programs were installed in some customer server environments.
Those are two different findings.
The first describes the potentially exposed population. The second confirms malicious software installation within a subset of the environment.
The company has not published a complete list of infected servers, malware samples or confirmed customer victims.
As a result, headlines claiming 26,739 confirmed malware infections would overstate the available evidence.
Customers should nevertheless treat credentials and other sensitive information stored on their affected servers as potentially exposed until the investigation provides more detail.
Why GMO Internet Shut Down Its Desktop Cloud Service
The shutdown was a containment decision made during an active security investigation.
When malicious programs are found inside hosted server environments, a provider must consider whether compromised systems can continue exposing stored information or support additional unauthorized activity.
Stopping affected infrastructure can help interrupt ongoing attacker access and prevent potentially compromised workloads from continuing normal operations.
However, shutting down customer servers also creates significant service disruption.
Customers running scheduled applications, remote desktop sessions or automated processes may lose access to those workloads until services are restored.
The October 21 notice confirms that the interruption affects every Desktop Cloud plan.
It does not establish that all individual servers were equally compromised.
Nor does it confirm that other Onamae.com products, including its separate domain registration and hosting services, were affected by the same shutdown.
Customers should check the provider’s official notice page for service restoration updates rather than relying on an assumed reopening time.
Why MetaTrader and Automated Trading Users Are Concerned
Onamae Desktop Cloud is used for persistent remote application hosting, including automated foreign exchange trading workloads.
The service is marketed for running platforms such as MetaTrader 4, which can execute automated trading strategies while the customer’s personal computer is switched off.
A cloud service disruption can therefore interrupt more than simple remote desktop access.
For traders who rely on automated execution, a stopped virtual server may prevent trading software from carrying out its normal scheduled operations.
Potential access to stored files adds a separate account-security concern.
Users may have stored trading platform credentials, remote desktop passwords or other account information inside the affected environment.
GMO has not established that attackers executed unauthorized trades, obtained financial account access or altered trading positions.
Nevertheless, anyone using the affected service for trading should inspect their accounts and follow their broker’s credential-security recommendations.
Do not attempt to restore automation by reusing potentially exposed passwords on an unverified replacement server.
What Data Could Have Been Accessed?
GMO states that information stored on customer servers may have been viewed by an unauthorized third party.
The disclosure does not specify exactly which files or customer records were accessed.
Depending on how a customer configured their environment, a cloud server may contain:
- Remote desktop usernames and passwords.
- Saved application authentication credentials.
- Trading platform login information.
- Configuration files containing secrets.
- Application data and locally stored documents.
- Service access tokens or API keys.
These are examples of possible server-resident information, not a vendor-confirmed list of stolen data types.
GMO said it had not confirmed leakage of personal information held by the company or misuse of viewed information at the time of its announcement.
It also clarified that it does not retain customers’ payment-card information in the relevant manner.
This should not be confused with a finding that every credential stored inside an affected virtual server was protected.
Customers should assess their own data exposure based on what was actually stored in their cloud environments.
How Did Hackers Plant Malware on the Cloud Servers?
The exact intrusion mechanism has not been publicly established.
GMO Internet confirmed unauthorized access and installation of malicious programs, but its notice does not identify:
- The vulnerability or misconfiguration used for initial access.
- Whether stolen credentials played a role.
- The malware family or file names.
- Any command-and-control infrastructure.
- The attacker’s persistence mechanism.
- The source of the intrusion.
Those gaps matter because the remediation needed after a cloud compromise depends on which security boundary was crossed.
A compromised customer login requires different investigation from unauthorized access to underlying hosting infrastructure.
The available disclosure does not support assigning the incident to a known ransomware gang, espionage group or specific CVE.
Until technical findings are published, defenders should avoid treating speculative attack paths as confirmed facts.
Onamae Desktop Cloud Customers: What to Do Immediately
GMO’s immediate recommendation is to change credentials stored or used within affected servers.
Even if customers cannot currently connect to their Desktop Cloud environments, many related accounts can be secured directly through their respective service providers.
1. Change Stored and Reused Passwords
Identify remote desktop credentials, application logins and other authentication information that may have been available inside the server.
Change those passwords using trusted devices and the official account-management websites.
If the same password was reused on another service, change it there as well.
Use different passwords for unrelated accounts.
2. Secure Trading Accounts
Customers using MetaTrader or similar software should review their broker account security settings and available login protections.
Where supported, change trading and client portal passwords and enable multifactor authentication.
Check account activity and trading history for transactions or configuration changes that cannot be explained.
Report suspicious activity directly to the broker.
3. Rotate API Keys and Application Secrets
If the affected server stored API tokens, database passwords or other service credentials, revoke or rotate them at the issuing service.
Updating a local configuration file does not revoke a previously issued credential.
Record which applications use each secret so legitimate services can be restored with replacement credentials later.
4. Monitor for Phishing
GMO warns that attackers may exploit the incident by sending messages pretending to provide account verification or recovery instructions.
The provider specifically states that it will not ask customers for passwords or credit card information by email or telephone.
Customers should navigate directly to the official Onamae.com website instead of entering credentials through unexpected recovery links.
5. Preserve Evidence and Incident Records
Keep copies of relevant official notifications, account activity records and support correspondence.
When the service becomes available, do not immediately run unfamiliar executables or delete suspicious files before a security investigation.
For business-critical environments, document what applications and credentials were present on the affected servers.
How to Investigate a Potentially Compromised Cloud Server
Customers who regain access to a previously affected machine should not assume the shutdown removed malicious software.
A provider-wide interruption is not proof of individual host remediation.
Before restoring sensitive workloads, request information about the provider’s investigation and recovery process.
Review Authentication and Administrative Changes
Where reliable logs are available, investigate unexpected successful logins, changes to administrator accounts and unfamiliar remote sessions.
On Windows environments, relevant evidence may include Security Event Logs, remote desktop authentication records and account-management events.
For example, Windows Security Event ID 4624 records successful logon events, while Event ID 4625 records failed logon attempts when appropriate auditing is enabled.
Neither event type independently proves an intrusion.
Investigators must correlate account identity, logon type, timing and source details with expected operations.
Check Persistence and Application Integrity
If authorized forensic access is available, review scheduled tasks, startup entries, services, unexpected accounts and recently modified executables.
Preserve suspicious artifacts for analysis rather than assuming that every unfamiliar file is malicious.
Because GMO has not identified the malware, no specific hash, process name or removal command can be reliably recommended for this incident.
Prefer Trusted Recovery for Confirmed Compromise
If a server is confirmed compromised, rebuild or restore it using a clean and validated recovery method rather than relying solely on deleting a suspected executable.
Rotate credentials that the compromised environment could access.
Verify operating-system updates, remote access settings and application configurations before reconnecting important services.
The exact recovery process should follow GMO’s official instructions and the customer’s own incident-response requirements.
How Can Businesses Reduce Cloud Hosting Risk?
Although the initial access method remains unknown, the incident demonstrates why hosted workloads need independent security and recovery planning.
Organizations should maintain reliable inventories of their hosted servers, installed applications and credentials.
Store secrets in purpose-built systems where supported rather than leaving reusable passwords in plaintext application files.
Limit the permissions of service accounts and tokens so that exposure of one credential does not automatically grant access to unrelated systems.
Enable multifactor authentication on administrative accounts wherever it is supported.
Keep recoverable backups separate from the operational environment and periodically test restoration procedures.
For continuously running trading or business applications, maintain a documented continuity plan for provider outages.
These are general risk-reduction measures. The published incident notice does not establish that a particular missing customer control caused this compromise.
Confirmed vs Unknown: What GMO Internet Has Established
Confirmed
- Unauthorized third-party access occurred within Onamae Desktop Cloud.
- Malicious programs were installed in some customer server environments.
- GMO identified 26,739 server environments as potentially affected.
- Stored server information may have been viewed.
- The company began shutting down servers on October 21 at 4:00 a.m. Japan time.
- The shutdown covers all Desktop Cloud plans.
- Customers were instructed to change potentially exposed credentials.
Unknown or Not Established
- The exact number of infected servers.
- The number of affected customer accounts.
- The malware family, capabilities or persistence method.
- The initial access vector or exploited CVE.
- The identity of the attacker.
- Confirmed data misuse or unauthorized financial transactions.
- A final service restoration date in the October 21 notice.
- Whether every affected host has been fully remediated.
CyberUpdates365 Analysis
The Onamae incident illustrates a major operational challenge in cloud security: a hosting environment can be affected by malicious activity even when individual customers have not changed their applications.
The precise compromise mechanism is not yet known, so it would be premature to assign responsibility to a specific administrative control.
However, the incident demonstrates why customers need visibility into the security of both their own workloads and the hosting services they depend on.
The distinction between 26,739 potentially affected servers and the smaller, unspecified set with confirmed malicious programs is especially important.
A precautionary infrastructure shutdown can be justified by uncertainty, but uncertainty should not be converted into a false count of confirmed infections.
The possible exposure of stored credentials creates an additional problem.
Even after servers are restored, an attacker who obtained valid passwords or tokens may retain access to connected services unless those credentials are revoked.
For that reason, incident recovery has at least two parts: ensuring systems are trustworthy and ensuring potentially exposed identities can no longer be misused.
Customers running automated trading software face a third problem: maintaining business continuity while cloud workloads are offline.
A replacement infrastructure provider may restore application availability, but moving a workload without addressing exposed secrets can carry the same security risk into the replacement environment.
At the same time, businesses should avoid rushing unverified backups or potentially infected application files onto clean servers.
The best recovery sequence involves preserving evidence, verifying provider guidance, rotating secrets, restoring from trusted sources and monitoring the resulting environment.
The central lesson is that cloud incident recovery requires coordinated infrastructure, identity and application security rather than simply turning servers back on.
Research Evidence
- Provider: GMO Internet / Onamae.com Desktop Cloud.
- Intrusion confirmed: October 20, 2026.
- Official disclosure: October 21, 2026.
- Potentially affected servers: 26,739.
- Confirmed malware installation: Some customer server environments.
- Server shutdown: From 4:00 a.m. JST on October 21.
- Shutdown coverage: All Desktop Cloud plans.
- Potentially accessed data: Information stored inside customer server environments.
- Confirmed misuse: Not established in the official notice.
- Attack method: Undisclosed.
- Malware family: Undisclosed.
- Restoration date: Not confirmed in the cited October 21 notice.
- Primary customer action: Change stored or reused authentication credentials.
Frequently Asked Questions
What happened to Onamae Desktop Cloud?
GMO Internet confirmed unauthorized access and installation of malicious programs in some customer server environments. The company suspended the service while investigating.
Were 26,739 servers infected with malware?
That has not been established. GMO identified 26,739 servers as potentially affected but confirmed malware installation only in some environments.
When did Onamae Desktop Cloud shut down?
GMO began progressively stopping servers on October 21, 2026, at 4:00 a.m. Japan Standard Time.
Was customer data stolen?
GMO said information stored on servers may have been viewed. Its October 21 notice did not confirm personal-data leakage or misuse of viewed information.
Does the shutdown affect all Onamae.com services?
The disclosed suspension covers all Desktop Cloud plans. It does not establish that every other Onamae.com service was shut down because of the incident.
Should affected customers change passwords?
Yes. GMO specifically advised customers to change authentication credentials stored or used on their cloud servers, including passwords reused on other services.
Is the malware identified?
No. The company’s official notice does not disclose a malware family, initial entry point or exploited vulnerability.
When will Onamae Desktop Cloud resume service?
The October 21 incident notice did not provide a confirmed restoration date. Customers should consult GMO’s official updates for the latest status.
Final Takeaway
The October 2026 Onamae Desktop Cloud incident is a confirmed unauthorized-access and malicious-program installation event affecting a Japanese cloud service used for persistent remote workloads.
GMO Internet identified 26,739 potentially affected server environments and suspended all Desktop Cloud plans while investigating.
Although stored information may have been viewed, the company has not established the full malware infection count or confirmed misuse of customer data.
Customers should rotate potentially exposed credentials, verify connected-account activity and follow official restoration guidance before returning important workloads to service.
The priority is to secure identities and restore trusted systems, not merely resume access to the affected cloud servers.
Could a cloud provider incident expose credentials stored by your applications?
GMO’s investigation highlights the risks of hosted environments and stored secrets. Our separate Railway security report explains how potentially exposed environment variables can create downstream credential-rotation and deployment challenges.
Read: Railway Security Incident May Expose Customer API Keys and Database Credentials →