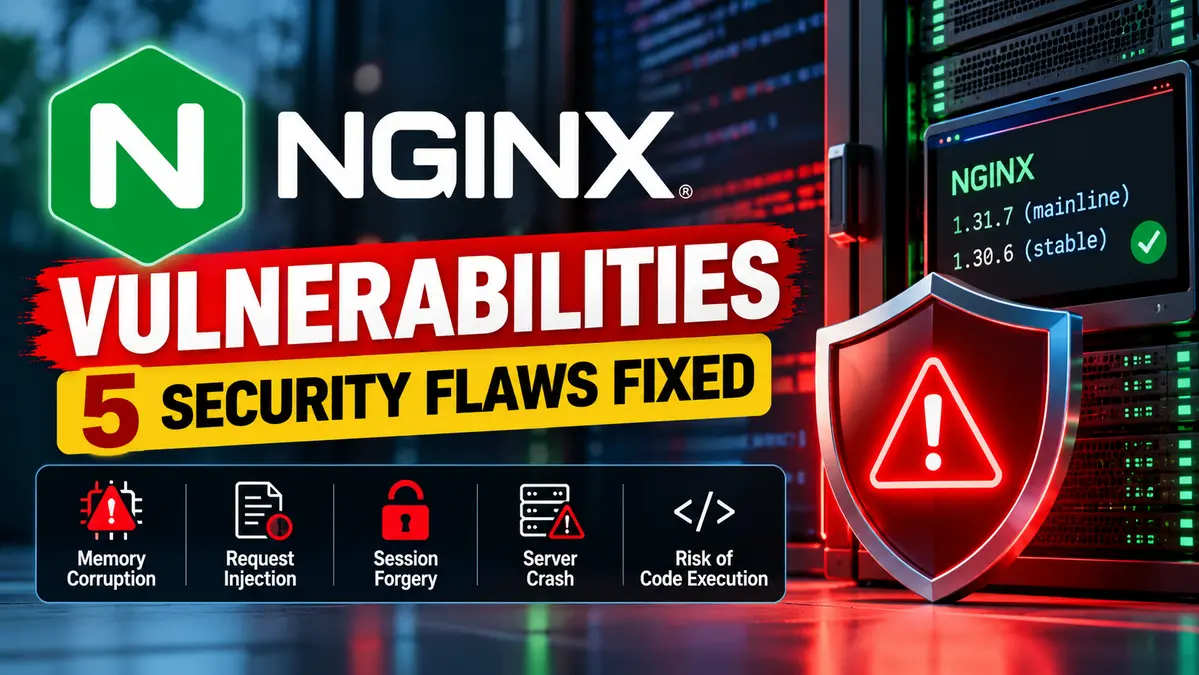
NGINX vulnerabilities fixed in the latest security update include five flaws affecting memory safety, HTTP/3 request handling and TLS session behavior, with several issues remotely triggerable under specific server configurations.
NGINX released versions 1.31.7 mainline and 1.30.6 stable on October 14, 2026 to address the newly disclosed security issues.
The official NGINX security advisory lists five CVEs fixed in the release: CVE-2026-15176, CVE-2026-93479, CVE-2026-95101, CVE-2026-97629 and CVE-2026-97205.
For broader enterprise vulnerability coverage and patching guidance, see our CVE and Vulnerability Exploits 2026 Hub.
Key Takeaway
The October NGINX security update fixes five vulnerabilities affecting NGINX Open Source and related products. Three of the issues are memory-safety flaws that can crash worker processes and may lead to code execution if additional exploitation conditions are met.
The remaining two vulnerabilities involve HTTP/3 request-body injection and TLS session forgery during ticket-key rotation.
Administrators should upgrade to NGINX Open Source 1.31.7 or 1.30.6, or install the corresponding fixed release supplied for NGINX Plus and related products.
NGINX Vulnerabilities Include 3 Memory-Safety Flaws
The three most serious issues highlighted in the latest disclosure are:
- CVE-2026-97205 — use-after-free involving asynchronous file I/O
- CVE-2026-93479 — buffer overflow during script evaluation
- CVE-2026-15176 — buffer overflow involving alias and rewrite configuration
All three can be triggered by specially crafted requests when the vulnerable server is running a matching configuration.
Successful exploitation can terminate or restart NGINX worker processes, and memory corruption may create a path toward code execution in more favorable exploitation conditions.
CVE-2026-97205 Affects AIO and SSI Processing
CVE-2026-97205 is a use-after-free vulnerability that affects NGINX when asynchronous file I/O is used together with Server Side Includes processing.
The issue affects vulnerable NGINX versions from 0.8.11 through 1.31.6.
NGINX lists versions 1.31.7 and later and 1.30.6 and later as not vulnerable.
The vulnerable condition involves a request path where an SSI page uses an include operation while AIO is enabled.
A worker process can continue referencing memory after it has already been released, creating a use-after-free condition.
That can result in memory corruption or an unexpected worker termination.
CVE-2026-93479 Causes Buffer Overflow in Script Evaluation
CVE-2026-93479 is a buffer overflow vulnerability involving NGINX script evaluation.
The official advisory lists the following affected Open Source versions:
- 1.31.2 through 1.31.6
- 1.30.0 through 1.30.5
The vulnerability is triggered only under certain configuration patterns involving variables and regular-expression captures.
Specifically, unsafe behavior can occur when configuration logic references regex capture variables in a way that causes the worker process to write beyond the intended memory allocation.
A crafted HTTP request can then trigger the vulnerable code path.
CVE-2026-15176 Affects alias and rewrite Configurations
CVE-2026-15176 is another buffer overflow vulnerability and affects a broader range of NGINX releases.
NGINX lists versions from 0.1.29 through 1.31.6 as vulnerable.
The issue occurs when a location configuration combines certain uses of alias, rewrite and request-filename evaluation.
A remotely supplied request can reach the unsafe path if the server configuration matches the vulnerable pattern.
As with the other memory-safety bugs, successful exploitation can crash a worker process and may potentially lead to more severe memory corruption outcomes.
Code Execution Is Possible Only in Certain Conditions
The presence of a memory corruption bug does not automatically mean every vulnerable NGINX server can be remotely taken over.
The three memory-safety flaws require specific server-side configurations that attackers cannot normally control directly.
In addition, reliable code execution may require defeating memory protections such as Address Space Layout Randomization, or ASLR.
Without those conditions, the more likely immediate effect is a worker-process crash and temporary service disruption.
This distinction is important because the vulnerabilities should not be described as universal unauthenticated remote code execution flaws.
Two Additional NGINX Vulnerabilities Were Fixed
The October 14 release also fixes two other security issues that were not the main focus of the memory-corruption reporting.
CVE-2026-95101 — HTTP/3 Request Body Injection
CVE-2026-95101 affects NGINX’s HTTP/3 functionality.
The official NGINX advisory describes the flaw as a request body injection vulnerability.
Affected versions are:
- 1.25.0 through 1.31.6
Versions 1.31.7 and 1.30.6 are not vulnerable.
CVE-2026-97629 — TLS Session Forgery
CVE-2026-97629 is a session-forgery issue related to TLS session-ticket key rotation.
The vulnerability affects NGINX versions:
- 1.23.2 through 1.31.6
As with the other October issues, upgrading to the fixed releases addresses the vulnerability.
NGINX 1.31.7 and 1.30.6 Contain the Fixes
NGINX released two fixed Open Source branches on October 14:
- NGINX 1.31.7 — mainline
- NGINX 1.30.6 — stable
The official NGINX release information confirms that these versions include fixes for the five newly disclosed vulnerabilities.
Administrators should not assume that an older package version from a Linux distribution is necessarily vulnerable or fixed solely from its visible version number.
Distribution vendors may backport individual security patches while retaining an older package version.
NGINX Plus and Related Products Are Also Affected
F5’s security guidance indicates that the same vulnerability classes can affect NGINX Plus and several products built around NGINX components.
Depending on the specific CVE, affected product families may include:
- NGINX Plus
- NGINX Instance Manager
- F5 WAF for NGINX
- NGINX Gateway Fabric
- NGINX Ingress Controller
Administrators using commercial or Kubernetes-focused NGINX products should review F5’s product-specific advisory rather than relying only on the Open Source version matrix.
Why Internet-Facing NGINX Servers Should Be Prioritized
NGINX is widely deployed as a web server, reverse proxy, load balancer and application-delivery layer.
That means vulnerable NGINX systems are often directly reachable from the public internet.
Even when a vulnerability primarily crashes worker processes, an attacker who can repeatedly trigger that condition may cause:
- Application outages
- Intermittent service availability
- Worker restarts
- Performance degradation
- Increased operational load
Memory-corruption vulnerabilities also deserve additional attention because exploitability can improve over time as researchers analyze the affected code.
Configuration Determines Exposure
Not every NGINX installation is exposed to all five vulnerabilities.
The three memory-safety bugs each depend on specific configuration conditions.
Administrators should therefore review both the installed version and the active configuration.
A useful starting point is:
nginx -TThis command prints the complete active NGINX configuration, including configuration files loaded through include directives.
Security teams can then compare the configuration against the conditions described in the relevant advisories.
How to Verify NGINX Configuration Safely
After changing an NGINX configuration, administrators should test it before reloading the service.
Use:
nginx -tA successful syntax check helps prevent accidental outages caused by configuration errors.
After applying a fixed package or configuration change, administrators should also verify that the expected NGINX binary and configuration are actually in use.
Temporary Mitigation for CVE-2026-97205
If immediate patching is not possible, administrators can reduce exposure to CVE-2026-97205 by disabling one of the features required for the vulnerable path.
This can include disabling:
- Asynchronous file I/O
- Server Side Includes
These changes can affect application behavior or performance, so they should be tested before production deployment.
Temporary Mitigation for CVE-2026-93479
For CVE-2026-93479, administrators should review configurations that use regular-expression captures inside map or related string expressions.
Using explicit named captures and ensuring they are referenced only inside the intended matching context can reduce exposure.
The permanent fix remains upgrading to a patched release.
Temporary Mitigation for CVE-2026-15176
Administrators should review location blocks that combine alias and rewrite behavior.
Where possible, avoid referencing $request_filename in vulnerable configuration contexts until the server can be patched.
Again, configuration workarounds should be treated as temporary risk reduction rather than a replacement for the security update.
NGINX and Apache Both Received Major Web Server Security Updates
The NGINX disclosure follows another major web-server security update covered by CyberUpdates365.
Apache recently released version 2.4.69 to fix 20 Apache HTTP Server vulnerabilities, including memory-safety flaws and configuration-dependent potential code execution.
The NGINX and Apache issues are unrelated, but both updates show why internet-facing web servers should be included in regular vulnerability-management and patching workflows.
No Active Exploitation Reported
The current NGINX security advisories do not state that the five October vulnerabilities are being actively exploited in the wild.
That means they should not be described as zero-days under active attack unless new evidence emerges.
However, public disclosure of affected versions and configuration conditions can make future exploit development easier.
What Administrators Should Do Now
Security and infrastructure teams should:
- Identify all NGINX Open Source and NGINX Plus deployments
- Upgrade Open Source systems to 1.31.7 or 1.30.6
- Review F5 advisories for NGINX Plus and related commercial products
- Run
nginx -Tto review the full active configuration - Check for AIO and SSI combinations
- Review
mapdirectives using regex captures - Review location blocks using
alias,rewriteand$request_filename - Check whether HTTP/3 is enabled
- Confirm TLS session-ticket key rotation settings
- Test configuration changes with
nginx -t - Verify patched binaries are active after upgrade
Frequently Asked Questions
How many NGINX vulnerabilities were fixed?
The October 14, 2026 NGINX release fixes five security vulnerabilities.
Which NGINX vulnerabilities can cause memory corruption?
CVE-2026-97205, CVE-2026-93479 and CVE-2026-15176 are memory-safety vulnerabilities involving use-after-free or buffer-overflow conditions.
Can the flaws allow remote code execution?
Some memory corruption conditions may potentially be exploitable for code execution, but successful exploitation requires specific server configurations and may also require bypassing memory protections such as ASLR.
Which NGINX versions contain the fixes?
NGINX Open Source 1.31.7 and 1.30.6 contain the October security fixes.
Are all NGINX servers vulnerable?
No. Exposure depends on both the installed version and the active server configuration.
Are attackers actively exploiting these flaws?
NGINX’s current advisory does not report active exploitation of the October vulnerabilities.
What is the fastest way to check the active configuration?
Administrators can run nginx -T to display the full active configuration and all included configuration files.
Final Takeaway
The latest NGINX vulnerabilities show why web-server security depends on both patching and configuration review.
NGINX 1.31.7 and 1.30.6 fix five security issues, including three memory-safety vulnerabilities that can crash worker processes and may create a path to code execution under specific conditions.
The release also fixes an HTTP/3 request-body injection flaw and a TLS session-forgery issue.
Administrators should upgrade affected systems, review active configurations and confirm that all internet-facing NGINX deployments are running a patched build.
There is currently no confirmed active exploitation of the five vulnerabilities.