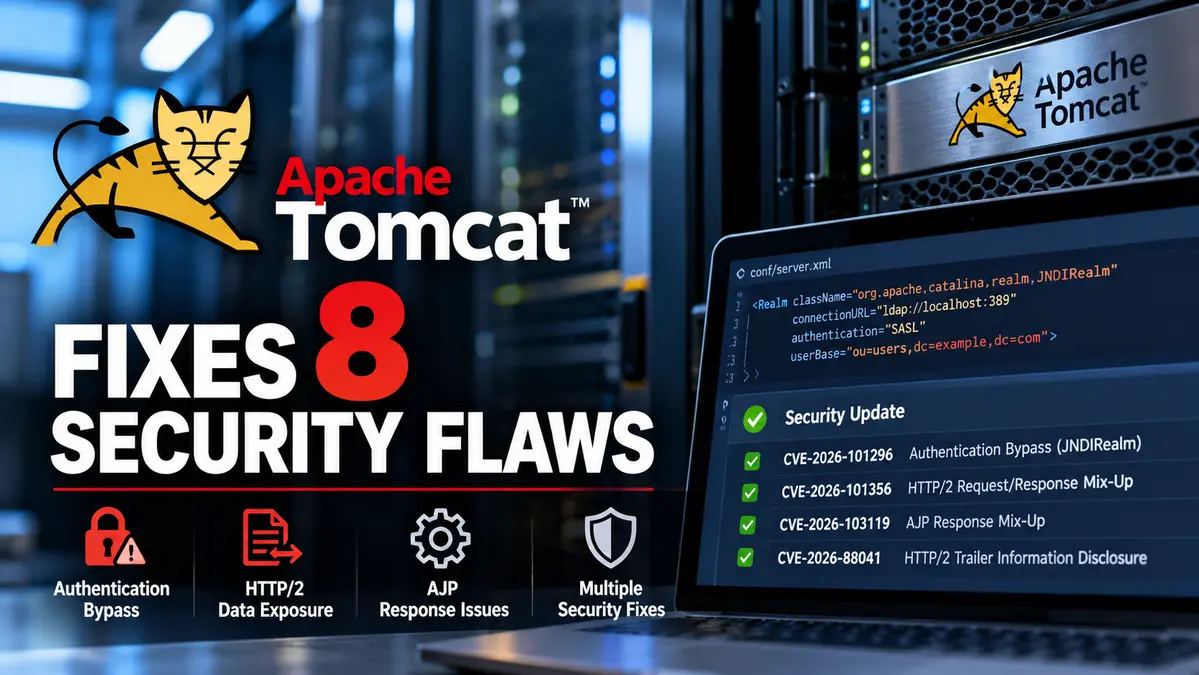
Apache Tomcat security flaws disclosed on October 20, 2026, include an authentication bypass that could let attackers sign in without a valid password, alongside HTTP/2 processing weaknesses that may mix requests or responses between users.
The Apache Software Foundation published details of eight vulnerabilities affecting different versions and configurations of its Java application server. Three are rated Important and five are rated Low.
Among the most concerning is CVE-2026-101296, which affects JNDIRealm configurations using non-GSSAPI SASL authentication mechanisms. Under those conditions, a missing credential-validation step can allow authentication to succeed without the correct password.
The issue is not a universal bypass affecting every Tomcat installation. Its impact depends on the authentication mechanism configured by the administrator.
Apache released fixes in Tomcat 11.0.27, 10.1.61 and 9.0.123. Administrators running affected builds should review the official advisories and confirm which features are enabled before applying updates.
For broader guidance on identifying and prioritizing enterprise vulnerabilities, see our CVE Vulnerabilities and Enterprise Security Hub.
Key Findings From the Apache Tomcat Security Update
- Public disclosure: October 20, 2026.
- Total vulnerabilities: Eight distinct CVEs across the affected branches.
- Severity: Three Important and five Low.
- Authentication bypass: CVE-2026-101296, affecting specific JNDIRealm SASL configurations.
- HTTP/2 request confusion: CVE-2026-101356 can cause requests or responses to become mixed between users.
- AJP response issue: CVE-2026-103119 affects Tomcat 11 and can cause response-body data to cross request boundaries.
- Additional issues: HTTP/2 trailer leakage, TLS failures, redirect processing, FIPS-mode fallback and Unix Domain Socket permissions.
- Fixed releases: Tomcat 11.0.27, 10.1.61 and 9.0.123.
- Exploit status: Apache’s advisories do not establish active exploitation of the disclosed flaws.
Apache Tomcat Security Flaws: All 8 CVEs Explained
The eight vulnerabilities affect different parts of Tomcat, from authentication and request processing to connector behavior and security configuration.
Apache’s severity classifications are based on the project’s own security impact assessment. They should not be confused with CVSS scores.
CVE-2026-101296: JNDIRealm Authentication Bypass
This Important vulnerability affects Tomcat’s JNDIRealm component when configured to authenticate using non-GSSAPI SASL mechanisms.
According to Apache, a required step in credential validation was missing.
As a result, an attacker could authenticate without supplying the correct password under the affected configuration.
This is a serious issue for environments using JNDIRealm to authenticate application users.
However, deployments that do not use the affected authentication mechanism should not be described as vulnerable to this specific bypass solely because they run Tomcat.
Affected versions:
- Tomcat 11.0.0-M1 through 11.0.26
- Tomcat 10.1.0-M1 through 10.1.60
- Tomcat 9.0.0.M1 through 9.0.122
Fixed in: 11.0.27, 10.1.61 and 9.0.123.
CVE-2026-101356: HTTP/2 Request and Response Mix-Up
The second Important vulnerability involves incorrect recycling and reuse of internal objects during HTTP/2 processing of asynchronous servlets.
When an error occurs during asynchronous request handling, Tomcat can incorrectly reuse processing state.
That behavior may cause a request or response to become mixed with another user’s request or response.
For applications handling user-specific information, such cross-user confusion can have confidentiality and integrity implications.
The vulnerability does not establish that every HTTP/2 response leaks information. Exploitation depends on the affected code path and processing conditions.
Affected versions:
- Tomcat 11.0.22 through 11.0.26
- Tomcat 10.1.55 through 10.1.60
- Tomcat 9.0.118 through 9.0.122
Fixed in: 11.0.27, 10.1.61 and 9.0.123.
CVE-2026-103119: AJP Response Mix-Up
CVE-2026-103119 is another Important vulnerability, affecting the AJP connector in Apache Tomcat 11.
A buffer under-read during a large non-blocking write can cause a response body to be divided between the current request and a later request using the same connection.
Apache says the most likely consequence is failure of the subsequent request, although information from the first response could also appear in the second.
The issue matters particularly in architectures where Tomcat communicates with a frontend web server through AJP.
Affected versions: Tomcat 11.0.0-M25 through 11.0.26.
Fixed in: Tomcat 11.0.27.
The official advisories do not list this CVE as affecting the Tomcat 9 or 10 branches.
CVE-2026-88041: HTTP/2 Trailer Header Leakage
This Low-severity vulnerability arises from incomplete cleanup of HTTP/2 trailer information.
Trailer fields belonging to an earlier request can become visible in a subsequent request.
Although Apache rates the issue Low, applications that use trailer fields for processing decisions should still apply the relevant fix.
The issue affects specified versions of Tomcat 9, 10 and 11, with exact ranges listed in Apache’s branch-specific advisories.
CVE-2026-93446: Intermittent TLS 1.3 Failures
CVE-2026-93446 involves incomplete cleanup that can cause TLS 1.3 connections to fail intermittently.
Apache rates the issue Low.
The principal reported consequence is unreliable connection handling rather than a documented authentication bypass or private-key disclosure.
Administrators investigating unexpected TLS errors should consider whether their installed Tomcat version falls within the affected range.
CVE-2026-74049: Jasper Redirect Processing
This vulnerability affects the Jasper JSTL replacement implementation of the <c:redirect> tag.
Processing may continue after a redirect instead of terminating the remainder of the page as expected.
That could produce unintended application behavior where later page operations should not execute.
The actual security impact depends on how an application uses the affected JSP functionality.
CVE-2026-74048: FIPS Activation Failure
CVE-2026-74048 concerns Tomcat installations configured to use the OpenSSL-FFM implementation with FIPS mode enabled.
If FIPS activation fails, the affected implementation can log an error but continue startup using JSSE in non-FIPS mode.
This can violate the operator’s expected cryptographic configuration.
The issue is especially relevant to environments requiring specific cryptographic operating modes for security or compliance purposes.
Administrators should verify actual runtime cryptographic settings rather than assuming that the presence of a FIPS configuration guarantees successful activation.
CVE-2026-80353: APR Unix Domain Socket Permission Race
The eighth vulnerability is a Low-severity race condition affecting the APR connector in Apache Tomcat 9.
During Unix Domain Socket creation, a timing issue can allow an unauthorized local user to access the socket.
Apache explains that an earlier fix for CVE-2026-65183 did not address the APR connector.
Affected versions: Tomcat 9.0.47 through 9.0.122.
Fixed in: Tomcat 9.0.123.
The attacker condition is local access. The issue should not be presented as a universally exploitable remote vulnerability.
Which Apache Tomcat Versions Are Fixed?
Apache published the October fixes across three maintained release branches.
- Tomcat 11: Upgrade affected installations to 11.0.27 or a later fixed release.
- Tomcat 10.1: Upgrade affected installations to 10.1.61 or a later fixed release.
- Tomcat 9: Upgrade affected installations to 9.0.123 or a later fixed release.
The releases are dated October 12, 2026, while the security disclosures were made public on October 20.
Not every CVE applies to all three branches. Administrators should use the appropriate branch-specific security page to determine which issues affect their installation.
Older unsupported Tomcat branches require separate attention. An unsupported deployment should not be assumed safe simply because the latest advisories do not list its versions.
How the Tomcat Authentication Bypass Affects Enterprise Applications
JNDIRealm allows Tomcat applications to authenticate users against directory services.
In affected deployments, the specific SASL mechanism determines whether CVE-2026-101296 is relevant.
The vulnerability is concerning because authentication is a primary boundary separating users from protected application functions.
If credential validation can succeed incorrectly, the application may grant access without the expected password check.
However, that does not mean the attacker automatically receives administrator privileges.
The resulting authorization depends on the application, directory configuration, mapped roles and account context.
Administrators should inspect the actual Realm implementation and authentication settings rather than relying only on application login-page behavior.
HTTP/2 and AJP Risks: Why Request Boundaries Matter
The HTTP/2 and AJP issues reveal a different class of security problem.
Application servers frequently process many concurrent requests and reuse internal objects to reduce overhead.
That optimization requires careful cleanup so that data associated with one request cannot influence another.
When request or response state is reused incorrectly, information may cross boundaries between users or connections.
For organizations processing authenticated sessions, sensitive application data or business transactions, such behavior deserves investigation.
The exact impact varies by protocol, Tomcat version and application configuration.
Security teams should avoid assuming that every response-processing vulnerability provides full system takeover. Apache’s descriptions support more specific outcomes involving request confusion, response leakage and connection failures.
How Administrators Can Detect Affected Tomcat Installations
Organizations should begin by determining which Tomcat versions and connector configurations are deployed.
1. Verify the Installed Version
For a standard Tomcat installation, administrators can use its version script:
$CATALINA_HOME/bin/version.shFor Windows installations, use the corresponding version.bat script.
Environment variables and installation paths differ between standalone, package-managed, containerized and embedded deployments.
Security teams should include embedded Tomcat instances and vendor-managed application packages in the inventory.
2. Review JNDIRealm Authentication Settings
Inspect the application’s Realm configuration and identify whether it uses the affected non-GSSAPI SASL mechanisms.
Do not assume that every directory-backed login uses the vulnerable configuration.
Document which applications depend on the affected Realm and whether their authentication boundary can be reached by untrusted users.
3. Identify Enabled Connectors
Determine whether HTTP/2, AJP and the relevant APR or OpenSSL-FFM components are active.
Review the effective server configuration, including settings applied by deployment tooling or application packaging.
A disabled or unused feature can change exposure, but it does not remove the need to evaluate other vulnerabilities affecting the same installation.
4. Correlate Application and Server Logs
Review authentication events, HTTP/2 processing errors, connector failures and unusual application behavior.
Indicators such as unexpected successful logins, unexplained connection failures or reports of mismatched response data may justify investigation.
These symptoms are not unique indicators of the October vulnerabilities and should not be treated as proof of exploitation.
How to Patch Apache Tomcat Safely
Administrators should follow Apache’s official upgrade instructions for the relevant branch and deployment method.
For a standalone installation, upgrading generally requires preparing a new Tomcat distribution, preserving appropriate application configuration and migrating application artifacts through a controlled procedure.
Containerized workloads should use an updated base image whose embedded Tomcat version contains the relevant fixes.
Where Tomcat is bundled with a commercial application, administrators should check the supplier’s compatibility and update guidance before replacing the embedded server.
A practical change plan should include:
- Inventory Tomcat instances, versions and hosting locations.
- Identify affected security configurations and enabled connectors.
- Review the Apache advisories for the relevant branch.
- Back up application configurations and prepare a rollback plan.
- Test the updated release against the deployed applications.
- Install the applicable fixed build or vendor-supported update.
- Restart or redeploy the affected service as required.
- Verify authentication, HTTP/2 traffic, AJP integrations and business-critical workflows.
Restricting affected interfaces can help reduce exposure while updates are prepared, but configuration changes should not be treated as a universal replacement for the official fixes.
Patch Verification: Confirm the Vulnerabilities Are Fixed
After deployment, confirm that the application server is actually running the expected version.
Do not rely only on the version of a downloaded archive or a newly built container image.
Verify the deployed process or running image, especially in environments containing multiple Tomcat installations.
Administrators should also test the components associated with the disclosed weaknesses.
- Authentication: Verify that affected JNDIRealm configurations reject invalid credentials.
- HTTP/2: Confirm normal handling of asynchronous requests and responses.
- AJP: Test relevant frontend-to-Tomcat integrations after upgrading Tomcat 11.
- TLS: Review connection errors and verify the intended cryptographic configuration.
- FIPS: Confirm FIPS mode actually activates when required.
- Socket permissions: Review permissions on applicable Unix Domain Socket configurations.
Testing should occur in an authorized environment and should avoid exposing sensitive application data.
If security logs or other evidence indicate a previous compromise, patching alone may not be sufficient.
Incident responders should investigate unauthorized access, affected accounts, session activity and possible information exposure.
Confirmed vs Unknown: What Apache’s Advisories Establish
Confirmed
- Apache disclosed eight vulnerabilities on October 20, 2026.
- Three are rated Important and five Low.
- CVE-2026-101296 can bypass password validation in specific JNDIRealm configurations.
- CVE-2026-101356 can cause HTTP/2 request or response mixing.
- CVE-2026-103119 affects AJP response handling in Tomcat 11.
- The remaining vulnerabilities involve protocol cleanup, redirect processing, cryptographic configuration and local socket permissions.
- Fixed releases include Tomcat 11.0.27, 10.1.61 and 9.0.123.
Unknown or Not Established
- That attackers are actively exploiting these new CVEs.
- That every Tomcat installation is vulnerable to the authentication bypass.
- That every flaw affects all three maintained branches.
- That any of the eight issues necessarily provides remote code execution.
- That customers have suffered confirmed data theft through these newly disclosed vulnerabilities.
- That the local APR socket race can be exploited remotely without additional conditions.
CyberUpdates365 Analysis
The October Tomcat disclosures show how security boundaries can fail in parts of application-server infrastructure that administrators rarely inspect during routine application development.
The authentication bypass is the clearest example.
An application may have carefully designed login and authorization workflows, but those controls depend on the underlying authentication provider functioning correctly.
When password validation fails open under a particular configuration, the weakness exists below the application’s normal business logic.
The HTTP/2 and AJP findings illustrate another risk: performance optimizations and protocol handling must preserve strict separation between requests.
Object reuse is useful for efficiency, but it introduces security consequences when processing state is not reset correctly.
For security teams, the practical lesson is that version information alone does not provide a complete exposure assessment.
Teams also need to know which Realms, connectors and protocol features are active.
This becomes especially important in containerized environments and vendor-managed applications where Tomcat may operate as an embedded dependency.
The eight CVEs have different prerequisites, but the remediation strategy remains consistent: identify the actual deployed components, apply the appropriate fixed release and verify behavior after the change.
Apache Tomcat’s October fixes reinforce that application security depends on the server’s authentication, protocol handling and runtime configuration, not just the code deployed on top of it.
Research Evidence
- Vendor: Apache Software Foundation.
- Public disclosure: October 20, 2026.
- Fixed releases dated: October 12, 2026.
- Number of vulnerabilities: Eight.
- Severity: Three Important, five Low.
- Tomcat 11 fixed version: 11.0.27.
- Tomcat 10.1 fixed version: 10.1.61.
- Tomcat 9 fixed version: 9.0.123.
- CVE-2026-101296: JNDIRealm authentication bypass.
- CVE-2026-101356: HTTP/2 asynchronous processing request/response mix-up.
- CVE-2026-103119: AJP response mix-up in Tomcat 11.
- CVE-2026-88041: HTTP/2 trailer information leakage.
- CVE-2026-93446: TLS 1.3 connection failures.
- CVE-2026-74049: Jasper redirect processing issue.
- CVE-2026-74048: FIPS activation failure handling.
- CVE-2026-80353: APR Unix Domain Socket permissions race in Tomcat 9.
- Confirmed active exploitation: Not established by Apache’s advisories.
Frequently Asked Questions
How many Apache Tomcat vulnerabilities were fixed in October 2026?
Apache disclosed eight vulnerabilities on October 20, 2026. Three are rated Important and five Low.
Which Tomcat versions contain the fixes?
The fixes are available in Tomcat 11.0.27, 10.1.61 and 9.0.123. Administrators should use the appropriate release for their supported branch.
Can the Tomcat authentication bypass work without a password?
Yes, under affected JNDIRealm configurations using non-GSSAPI SASL authentication mechanisms. It does not apply universally to every Tomcat authentication configuration.
What is CVE-2026-101356?
It is an HTTP/2 processing vulnerability involving incorrect object recycling that can cause request or response information to become mixed between users under specific error conditions.
Does CVE-2026-103119 affect Tomcat 9?
No. Apache lists CVE-2026-103119 as affecting specified Tomcat 11 releases.
Are these vulnerabilities being actively exploited?
Apache’s October security notices do not establish confirmed active exploitation of the newly disclosed issues.
Can upgrading Tomcat fix all eight vulnerabilities?
Upgrading to the appropriate fixed release addresses the relevant vulnerabilities in that branch. Administrators should still verify that the deployed application is running the updated version.
How can administrators check the Tomcat version?
Standard installations provide a version script under $CATALINA_HOME/bin/. Embedded, packaged and containerized deployments may require different inventory methods.
Final Takeaway
Apache Tomcat has released fixes for eight security vulnerabilities involving authentication, HTTP/2 processing, AJP response handling and other runtime components.
The most concerning is CVE-2026-101296, which can allow authentication without a valid password when JNDIRealm uses specific SASL configurations.
Separate protocol-processing flaws can also allow information to cross request boundaries under certain conditions.
Administrators should review their Tomcat branch, deployed version and enabled features before upgrading to the relevant fixed release.
The priority is to verify both the installed patch level and the configuration that determines whether each vulnerability is exploitable.
Is your enterprise vulnerability inventory missing application-server dependencies?
The Tomcat advisories show why server versions and runtime configuration matter. Explore our enterprise CVE hub for vulnerability investigations, patching guidance and remediation resources.
Read: CVE Vulnerabilities 2026 — Enterprise Security Hub & Fixes →