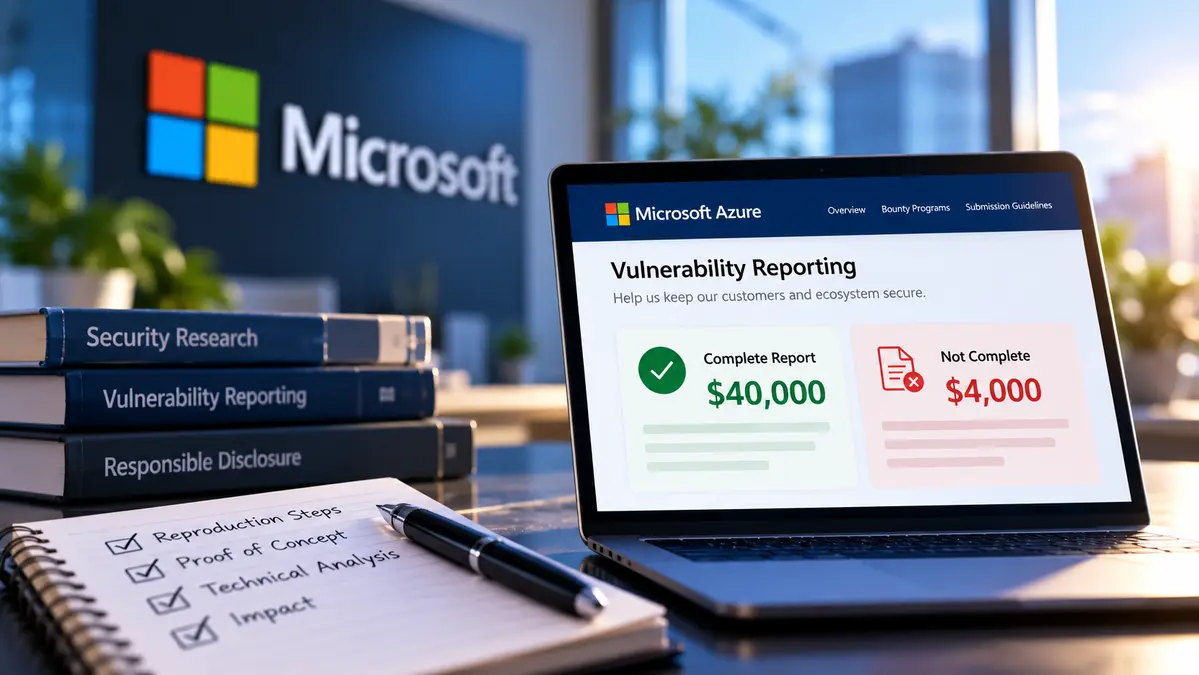
Microsoft bug bounty rewards now carry a sharper distinction between complete and incomplete vulnerability reports, with eligible critical Azure findings potentially earning $40,000 when submitted with the required evidence, compared with $4,000 when the initial report is assessed as Not Complete.
The change is part of a new assessment system introduced by the Microsoft Security Response Center (MSRC) on October 20, 2026. Microsoft is replacing several report-quality levels with two classifications: Complete and Not Complete.
For security researchers, the difference is significant. A technically valid vulnerability may still receive a lower eligible award if the original submission lacks reproduction steps, technical analysis or supporting artifacts required by the program.
Microsoft says the change is intended to help engineering teams verify reported vulnerabilities faster and reduce repeated requests for missing information.
But there is an important qualification: the $40,000 figure applies to specific eligible Azure vulnerability categories and severity levels. Microsoft is not promising that amount for every report, and a Complete assessment does not guarantee payment.
The policy also raises a practical question for ethical hackers: how much evidence should researchers prepare before reporting a serious security flaw?
For broader context on how security teams identify and validate enterprise vulnerabilities, see our CVE Vulnerabilities and Enterprise Security Hub.
Key Technical Findings
- Official announcement: Microsoft Security Response Center, October 20, 2026.
- New assessments: Complete and Not Complete replace the previous multi-level report-quality approach across Microsoft bounty programs.
- Effective date: Reports submitted on or after October 20, 2026, at 8 AM Pacific Time.
- Previous submissions: Reports submitted before the cutoff remain under earlier report-quality requirements.
- Azure critical RCE: General award of $40,000 for Complete versus $4,000 for Not Complete.
- Azure critical privilege escalation: The same $40,000 versus $4,000 distinction.
- Core evidence: Reproduction steps, a reliable proof of concept, vulnerability analysis, affected environment, exploit conditions and demonstrated impact.
- Submission rule: Completeness is assessed using evidence present in the initial report.
- AI-assisted research: Microsoft permits AI use but still requires accurate technical explanations and reproducible evidence.
- Important limitation: Completeness does not determine vulnerability severity or guarantee a bounty.
Microsoft Bug Bounty Rewards Now Depend on Report Completeness
Microsoft has formally introduced a simpler framework for evaluating the information submitted by external security researchers.
Previously, different bounty programs used multiple quality levels to assess research submissions.
Under the updated approach, reports receive one of two completeness assessments.
A Complete report includes the information and supporting evidence required for Microsoft engineers to understand, reproduce and assess the vulnerability with little or no additional follow-up.
A Not Complete report is missing at least one applicable requirement.
The assessment is separate from the vulnerability’s security severity and exploit impact.
That distinction matters because researchers may identify a serious security weakness while submitting insufficient documentation to establish how it works.
Microsoft can still investigate the issue, but the eligible bounty may be lower than it would have been for a submission containing the complete required evidence.
Microsoft announced that the new requirements apply to vulnerability reports submitted from October 20, 2026, at 8 AM Pacific Time.
Reports submitted before that cutoff continue under the previous requirements.
Azure Bug Bounty: $40,000 vs $4,000 for Critical Vulnerabilities
The Microsoft Azure Bounty Program provides one of the clearest examples of how the assessment affects potential payments.
Under the current general-award table, an eligible critical remote code execution vulnerability carries a $40,000 Complete award and a $4,000 Not Complete award.
Critical elevation-of-privilege findings have the same award distinction.
These amounts are tied to the specific Azure program, vulnerability impact and severity category.
They should not be interpreted as universal payout amounts across all Microsoft products.
Azure General Award Examples
- Critical remote code execution: $40,000 Complete; $4,000 Not Complete.
- Important remote code execution: $30,000 Complete; $3,000 Not Complete.
- Critical elevation of privilege: $40,000 Complete; $4,000 Not Complete.
- Important elevation of privilege: $10,000 Complete; $1,000 Not Complete.
- Critical information disclosure: $12,000 Complete; $1,200 Not Complete.
- Critical spoofing or tampering: $8,000 Complete; $800 Not Complete.
Azure’s published award range remains $400 to $60,000, and Microsoft retains discretion over awards under its program terms.
Some qualifying high-impact scenarios can also carry percentage multipliers.
For example, the Azure Bounty Program lists additional incentives for eligible Azure Kubernetes Service findings and certain Azure Key Vault scenarios.
Those multipliers depend on the applicable program conditions and should not be assumed for every report.
The broader point is that report completeness now has a clearly defined financial consequence within the published award structure.
What Makes a Microsoft Vulnerability Report Complete?
Microsoft’s updated submission guidance identifies several essential components of a Complete report.
The goal is straightforward: an engineer who has never encountered the issue should be able to reproduce and assess it using the original submission.
1. Clear Steps to Reproduce
Researchers must describe how to reproduce the finding from a known starting state.
The instructions should identify the relevant configuration, environment and actions needed to observe the security issue.
Vague descriptions that require an engineer to guess the missing steps may not satisfy the completeness requirements.
2. A Reliable, Minimized Proof of Concept
A proof of concept should demonstrate the reported behavior in a reproducible manner.
Where practical, researchers should minimize unnecessary code and dependencies so investigators can isolate the relevant issue.
A complex toolchain is not automatically better evidence than a smaller demonstration that clearly reproduces the vulnerability.
3. Accurate Vulnerability Classification
The report must identify the type of vulnerability.
This could include remote code execution, privilege escalation, information disclosure or another class supported by the relevant program.
The classification must match the behavior actually demonstrated.
A report showing limited information exposure should not describe the finding as full system compromise unless the evidence supports that impact.
4. Detailed Technical and Root-Cause Analysis
Microsoft expects researchers to explain the technical behavior responsible for the issue, including the root cause to the extent possible.
A strong explanation helps engineering teams understand which security boundary failed and which component may need remediation.
Unsupported assumptions about implementation details should be distinguished from behavior directly demonstrated by testing.
5. Affected Environment and Versions
Researchers must identify the relevant product, platform, configuration and version information.
For Azure bounty eligibility, Microsoft also requires qualifying vulnerabilities to be reproducible on the latest fully patched in-scope service or product.
An issue demonstrated only against an outdated or unsupported configuration may have different eligibility implications.
6. Exploitability and Attack Preconditions
The report should explain what an attacker would need to exploit the vulnerability.
Relevant conditions may include authentication, required permissions, network exposure, user interaction or a particular service configuration.
This allows Microsoft to distinguish practical exploitation paths from theoretical possibilities.
7. Demonstrated Security Impact
A Complete report must explain what an attacker could accomplish and what security boundary would be affected.
That impact should be supported by the proof of concept and associated artifacts.
When a larger impact is hypothetical, the report should distinguish it from what the researcher actually demonstrated.
Supporting Evidence Depends on the Vulnerability Type
Microsoft does not require exactly the same artifacts for every security finding.
The additional evidence depends on the product area and vulnerability class.
For example, memory-corruption vulnerabilities in endpoint or on-premises products may require crash dumps, call stacks and proof-of-concept source code.
File-redirection issues may require Process Monitor logs.
NTLM coercion or relay findings may require packet captures or other evidence demonstrating the authentication behavior.
Web application vulnerabilities have different requirements.
Microsoft’s guidance identifies evidence such as videos, HTTP requests and responses, Burp Suite logs, HAR files, network traces and supporting scripts.
These artifacts help investigators confirm that a security impact occurred rather than relying exclusively on the researcher’s description.
AI vulnerability reports must also follow Microsoft’s applicable AI security reporting guidelines.
The correct approach is to review the requirements for the specific bounty program and vulnerability category before preparing the final submission.
Why Adding Missing Evidence Later May Not Increase the Award
One of the most consequential details of the new policy concerns when evidence must be submitted.
Microsoft states that a report’s Complete or Not Complete assessment is based on the information and supporting artifacts included with the original submission.
Additional material provided after submission, including responses to follow-up requests from MSRC, does not change that initial completeness assessment.
This means researchers should avoid relying on later correspondence to supply essential reproduction steps or mandatory supporting files.
That does not mean Microsoft will stop investigating an initially incomplete vulnerability report.
The company continues to encourage disclosure of valid security issues even when researchers cannot satisfy every completeness requirement.
But researchers seeking the higher eligible award should review the report carefully before its initial submission.
The MSRC Researcher Portal Fields Matter
Microsoft also clarifies that uploading a detailed report as an attachment is not a substitute for completing the required Researcher Portal fields.
The core reproduction steps, technical details and impact explanation must be entered into the appropriate submission sections.
Supporting files can be attached where required, but researchers should not make investigators search an external document to discover information that belongs in the form itself.
Microsoft recommends keeping narrative sections focused and reasonably concise, with approximately 5,000 characters as general guidance rather than a strict limit.
The objective is to provide enough technical detail to reproduce the issue without overwhelming the submission with unrelated material.
Researchers should therefore prepare their evidence before opening the final submission workflow.
Does a Complete Report Guarantee a Microsoft Bounty?
No. Microsoft explicitly separates the completeness assessment from bounty eligibility and vulnerability severity.
A report can be technically well documented while describing behavior that is out of scope or does not demonstrate a qualifying security impact.
For the Azure program, eligible findings generally need to demonstrate a previously unknown Critical or Important vulnerability affecting an in-scope product or service.
The issue must also be reproducible on the latest, fully patched version.
Microsoft may reject a report that does not satisfy its eligibility conditions, regardless of how thoroughly the researcher documents it.
Similarly, a Complete assessment does not turn an Important vulnerability into a Critical one.
Severity, security impact, scope and completeness remain separate elements of the final award decision.
Why Microsoft Is Changing Its Reporting Process
Microsoft says vulnerability triage becomes slower when incoming reports lack essential information.
Security engineers may need to request missing steps, reconstruct the environment or determine whether a claimed exploit actually demonstrates a meaningful security impact.
That additional work can delay assessment and coordination.
The new assessment framework provides researchers with clearer expectations before they submit findings.
Microsoft also highlights the growing influence of AI-assisted vulnerability research.
AI tools can help researchers discover potential weaknesses and prepare submissions at greater scale.
But an AI-generated description is not equivalent to a demonstrated vulnerability.
Microsoft continues to welcome responsible AI-assisted research while requiring accurate analysis and technical evidence.
Researchers are responsible for verifying the behavior their reports describe, even when an AI assistant helped identify or explain the finding.
How Researchers Can Prepare a Complete Azure Vulnerability Report
The new framework creates a practical checklist for researchers working within Microsoft’s authorized testing rules.
- Confirm the target product and reported behavior are within the current bounty program’s scope.
- Reproduce the vulnerability in an authorized test environment.
- Record the affected product, platform, version and relevant configuration.
- Document the minimum steps required to trigger the issue from a known state.
- Prepare a reliable proof of concept that demonstrates the supported security impact.
- Explain attacker prerequisites, authentication requirements and required privileges.
- Include the technical root-cause explanation to the extent supported by the evidence.
- Gather all mandatory logs, traces, scripts or other supporting files for the relevant vulnerability class.
- Complete the MSRC Researcher Portal fields rather than relying solely on attached documents.
- Review the entire submission before sending it, because later evidence does not change its initial completeness assessment.
Researchers should not attempt to access customer information or exceed authorized testing boundaries merely to demonstrate a larger impact.
Microsoft’s Rules of Engagement require security testing to avoid unnecessary harm to customers, data and service availability.
If a researcher accidentally accesses unauthorized data, Microsoft’s guidance instructs them to stop, notify MSRC and handle the information according to the stated reporting requirements.
Confirmed vs Unknown: What Microsoft’s New Policy Establishes
Confirmed
- Microsoft introduced Complete and Not Complete report assessments across its bounty programs.
- The change applies to submissions made on or after October 20, 2026, at 8 AM Pacific Time.
- Earlier submissions remain subject to previous report-quality requirements.
- Azure’s general award table distinguishes substantially between Complete and Not Complete reports for eligible vulnerability categories.
- Initial evidence determines the completeness assessment.
- Severity and bounty eligibility are assessed independently.
- Microsoft continues to accept vulnerability reports that are Not Complete.
- AI-assisted reports must still contain accurate, reproducible technical evidence.
Not Established
- That every Azure vulnerability report qualifies for $40,000.
- That a Complete report automatically receives a bounty.
- That initially incomplete reports are ignored or discarded.
- That Microsoft has reduced the security severity of any particular vulnerability.
- That researchers must provide identical artifacts for every vulnerability type.
- That AI-generated vulnerability descriptions can replace independent technical validation.
- That the policy change was triggered by one specific security incident.
CyberUpdates365 Analysis
Microsoft’s new report-assessment framework changes the incentives surrounding vulnerability disclosure.
The discovery of a genuine security weakness is still central to bug bounty research. But the ability to demonstrate that weakness clearly now has a more explicit role in determining eligible rewards.
That could encourage researchers to prepare stronger evidence before submitting findings.
It also places greater importance on understanding the distinction between an observed vulnerability, a plausible exploitation scenario and a fully demonstrated security impact.
For security teams, the broader lesson is that useful vulnerability intelligence depends on reproducibility.
A vulnerability description may identify a concern, but engineering teams need to know which systems are affected, what conditions trigger the issue and whether the proposed impact can actually occur.
The policy also reflects the changing volume of AI-assisted security submissions.
AI can accelerate research workflows, but the final technical claims still require verification.
Making evidence quality part of the award structure gives researchers a direct reason to prioritize accurate, reproducible findings over submission volume alone.
There is a trade-off to consider.
Preparing complete supporting evidence can require additional time, particularly for complex vulnerabilities or findings that are difficult to reproduce.
Researchers must balance that effort against responsible disclosure timelines and the requirement to remain within authorized testing boundaries.
Microsoft continues to accept incomplete reports, which preserves a route for disclosing potentially important findings even when all required artifacts are unavailable.
The central lesson is that a vulnerability’s value to defenders depends not only on discovering it, but also on explaining and demonstrating it reliably.
Research Evidence
- Organization: Microsoft Security Response Center.
- Official announcement: October 20, 2026.
- New classifications: Complete and Not Complete.
- Policy effective: October 20, 2026, at 8 AM Pacific Time.
- Eligible Azure critical RCE: $40,000 Complete; $4,000 Not Complete.
- Eligible Azure critical elevation of privilege: $40,000 Complete; $4,000 Not Complete.
- Eligible Azure important RCE: $30,000 Complete; $3,000 Not Complete.
- Eligible Azure critical information disclosure: $12,000 Complete; $1,200 Not Complete.
- Azure published award range: $400 to $60,000, with additional awards possible under applicable terms.
- Mandatory evidence: Reproduction steps, proof of concept, vulnerability classification, technical analysis, affected environment, exploit conditions and impact.
- Additional artifacts: Depend on the affected product and vulnerability category.
- Initial submission requirement: Later evidence does not alter the original completeness assessment.
- Disclosure framework: Microsoft Rules of Engagement and Coordinated Vulnerability Disclosure.
Frequently Asked Questions
What changed in Microsoft’s bug bounty program?
Microsoft introduced Complete and Not Complete assessments for vulnerability reports submitted from October 20, 2026, at 8 AM Pacific Time. Report completeness can affect eligible bounty amounts.
Can researchers really earn $40,000 for an Azure vulnerability?
Yes. Microsoft’s Azure Bounty Program lists a $40,000 general award for eligible Complete reports involving critical remote code execution or elevation of privilege. Other requirements still apply.
Why would an incomplete Azure report receive only $4,000?
The Azure program’s general award table lists $4,000 for eligible Not Complete reports in those critical impact categories. This is a program-specific award distinction, not a guarantee of payment.
What makes a vulnerability report Complete?
A Complete report contains the applicable reproduction steps, reliable proof of concept, accurate technical analysis, affected environment, exploit conditions, demonstrated impact and supporting artifacts.
Can researchers submit missing evidence after filing a report?
Microsoft may request additional information, but material supplied after the original submission does not change the initial Complete or Not Complete assessment.
Does Microsoft reject all incomplete reports?
No. Microsoft says researchers should continue reporting security vulnerabilities even when they cannot provide every artifact required for a Complete assessment.
Can AI be used to discover vulnerabilities for Microsoft bounties?
Yes. Microsoft welcomes responsible AI-assisted research, but submissions must accurately describe the finding and include reproducible evidence.
Does a Complete report guarantee a bounty award?
No. Microsoft evaluates scope, severity, security impact and eligibility separately from report completeness.
Final Takeaway
Microsoft has introduced a new vulnerability-reporting assessment model that makes the completeness of a research submission a clearer factor in bounty awards.
Within the Azure program, eligible critical RCE and elevation-of-privilege reports can carry general awards of $40,000 when Complete and $4,000 when Not Complete.
However, the assessment does not guarantee payment or establish the severity of the finding.
For researchers, the practical priority is preparing reliable reproduction steps, technical analysis and mandatory supporting evidence before submitting.
A well-documented security finding gives engineers a clearer path from vulnerability discovery to effective remediation.
Finding a vulnerability is only the first step. Can your team prove its real security impact?
Microsoft’s reporting change highlights why reproducible evidence matters. Explore our enterprise vulnerability hub for technical investigations, affected-system guidance and remediation resources.
Read: CVE Vulnerabilities 2026 — Enterprise Security Hub & Fixes →