By Uday Patil, Cybersecurity Analyst
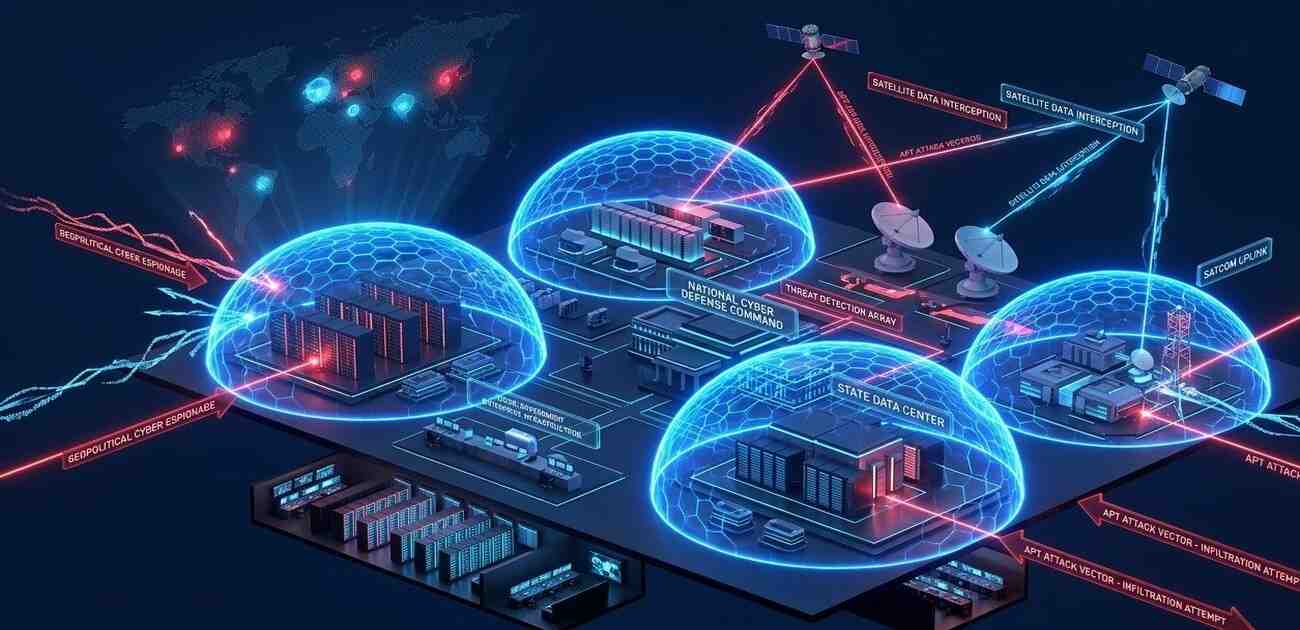
Analyzing nation state cyber warfare apt threats in 2026 reveals a permanent, dangerous escalation in state-sponsored digital espionage. Commercial enterprises and critical public infrastructure are no longer facing localized, independent hacking enthusiasts searching for transient recognition. Instead, modern enterprise networks are under constant siege by well-funded military cyber operations executed by highly disciplined state syndicates.
Advanced Persistent Threat (APT) groups affiliated with military intelligence agencies in Russia, China, and North Korea routinely compromise corporate networks. They utilize unpatched zero-day vulnerabilities, sophisticated social engineering, and stealthy malware to bypass traditional perimeter defenses. To survive, organizations must deploy proactive telemetry architectures and zero-trust frameworks to identify intrusions before hostile actors can extract proprietary intellectual property or disrupt administrative workflows.
In this master intelligence repository, we catalog confirmed state-sponsored cyber exploitation campaigns, break down tactical penetration methodologies across major geopolitical threat actors, and link directly to our deep technical forensic reports.
The Anatomy of Advanced Persistent Threats (APTs)
Before diving into specific geopolitical actors, network defenders must understand how nation state cyber warfare apt threats actually operate. Unlike smash-and-grab ransomware attacks, APT campaigns are designed for longevity and stealth.
- Phase 1: Reconnaissance and Weaponization. State-sponsored actors spend months mapping a target’s digital footprint. They identify vulnerable software supply chains, unpatched edge devices, and specific employees for spear-phishing campaigns.
- Phase 2: Initial Access and Evasion. Once a zero-day exploit or stolen credential grants access, the attackers deploy custom malware designed to evade standard endpoint detection and response (EDR) platforms.
- Phase 3: Lateral Movement and Persistence. The APT group moves silently across the network, escalating privileges and establishing multiple backdoor entry points to ensure they retain access even if one malware strain is discovered.
- Phase 4: Exfiltration. The ultimate goal is often data theft. Sensitive intellectual property, government communications, or financial data is encrypted, compressed, and slowly siphoned out of the network via covert command-and-control (C2) channels.
Russian APT Threat Groups & Geopolitical Surveillance
Russian state-sponsored defensive and offensive operations primarily target government defense suppliers, critical European communication networks, and global energy infrastructure. These russian apt threat groups rely on stealthy infiltration mechanisms to conduct long-term intellectual property interception and psychological operations.
FSB Cyber Espionage & Diplomatic Disruption
Military threat actors linked to Russian Federal Security Service (FSB) divisions routinely deploy persistent spyware against sensitive geopolitical infrastructure. Their campaigns are highly targeted, focusing on intelligence gathering rather than immediate financial gain. Inspect our deep investigation into Void Blizzard FSB Cyber Espionage & Obrezko Operations.
The Global Extortion & Ransomware Ecosystem
While strict military units handle espionage, global financial institutions frequently encounter coordinated ransomware extortion syndicates. While some of these groups operate from Eurasian territories with tacit state approval, others are western-based affiliates operating on a purely financial motive. Review our forensic profile on the extradition and legal prosecution of commercial extortionists in our Scattered Spider Hacker Peter Stokes Extradition Report.
North Korean Crypto Hackers & Financial Exploitation
Unlike other nations that focus primarily on traditional intelligence gathering, North Korean military hacking syndicates operate with a distinct and aggressive commercial financial goal. These units conduct massive cryptocurrency thefts and financial institution penetrations to circumvent international monetary trade sanctions.
Cryptocurrency Asset Harvesting
North korean crypto hackers actively compromise digital wallet platforms, decentralized finance (DeFi) exchange networks, and individual investors using highly targeted social engineering lures. Discover our verified technical exposure of North Korean Crypto Hackers & Financial Cyber Theft Campaigns.
Lazarus & Kimsuky Backdoor Architecture
Advanced units deploy custom remote access Trojan (RAT) executables disguised as developer employment test assignments or job recruitment documents. This tactic allows them to infiltrate enterprise code repositories and manipulate software supply chains. Examine our software analysis of Kimsuky & Lazarus Group Advanced Backdoor Toolkits.
Chinese Cyber Espionage & Zero-Day Weaponization
Chinese state-sponsored espionage networks systematically scan global corporate perimeters for vulnerable enterprise software infrastructure. The hallmark of chinese cyber espionage is the rapid weaponization of zero-day vulnerabilities and the execution of silent data exfiltration across commercial telecom networks and municipal services.
Below is our consolidated tracking of recent China-nexus infiltration vectors and campaigns:
- Cisco Edge Router Exploitation: Targeting Cisco Firewall and VPN telemetry gateways to establish permanent network footholds. Read the Cisco Zero-Day CISA Emergency Directive Alert.
- DLL Sideloading Weaponization: Hijacking legitimate Windows system library executables to load malicious payloads without triggering antivirus alerts. Review the China-Nexus DLL Sideloading Weaponization Guide.
- Email Infrastructure Breaches: Exploiting unpatched Roundcube webmail servers to intercept sensitive corporate and governmental communications. Analyze the Roundcube CVE-2024-42009 Chinese Hackers Report.
- HollowGraph Calendar C2 Exfiltration: Utilizing Microsoft 365 Cloud Calendar APIs to hide command-and-control traffic within legitimate cloud application data. Dive into the HollowGraph Microsoft 365 Malware Analysis.
Defending the Enterprise Against State-Sponsored Attacks
Commercial IT network defenders must elevate their security posture to combat these advanced adversaries. Traditional antivirus software and firewall rules are insufficient against customized malware and stolen legitimate credentials.
Modern enterprises must adopt a Zero Trust Architecture, which assumes that the network is always hostile. This involves implementing strict microsegmentation, enforcing phishing-resistant multi-factor authentication (MFA) via hardware security keys, and maintaining continuous, proactive threat hunting operations. Furthermore, organizations must drastically reduce their patching lifecycles, applying critical security updates to edge devices within hours rather than weeks.
Frequently Asked Questions: APT Threat Intelligence
What defines an Advanced Persistent Threat (APT) in 2026?
An Advanced Persistent Threat is a highly organized, state-sponsored or commercially sponsored cyber intrusion syndicate that gains undetected access to a computer network. These groups maintain illicit internal surveillance for months or years to harvest confidential data without triggering alarms.
Why do nation state cyber warfare apt threats target small businesses?
State intelligence operations exploit smaller commercial suppliers to perform stepping-stone supply chain intrusions. By compromising a weakly defended small business, they can seamlessly pivot into the networks of government defense manufacturers, federal software vendors, and primary financial settlement clearinghouses.
How does chinese cyber espionage differ from other state actors?
Chinese cyber espionage campaigns frequently focus on mass-scale intellectual property theft, economic espionage, and establishing long-term surveillance backdoors in global telecommunications and critical infrastructure equipment.
What is the primary goal of north korean crypto hackers?
The primary goal of north korean crypto hackers is to generate revenue for the state. By hacking cryptocurrency exchanges and decentralized finance protocols, they successfully steal billions of dollars to bypass strict international economic sanctions.
How can defenders consume actionable apt threat intelligence?
Organizations defend network perimeters by integrating real-time apt threat intelligence feeds into their Security Information and Event Management (SIEM) systems, adhering directly to emergency vulnerability remediation directives published by CISA, and conducting regular adversarial penetration testing.
Conclusion
The landscape of global cybersecurity has fundamentally shifted. As long as intellectual property holds value and digital infrastructure controls physical operations, state-sponsored cyber warfare will continue to dominate the threat horizon.
By understanding the distinct tactics of russian apt threat groups, chinese espionage units, and north korean financial syndicates, enterprise defenders can build resilient architectures capable of withstanding the inevitable breach attempts of 2026 and beyond.
Reported by CyberUpdates365 Threat Intelligence Desk
Delivering verified geopolitical cybersecurity intelligence, APT threat group profiling, and zero-day enterprise defense strategies. All structural countermeasures align directly with official United States CISA advisories and NIST cybersecurity frameworks.