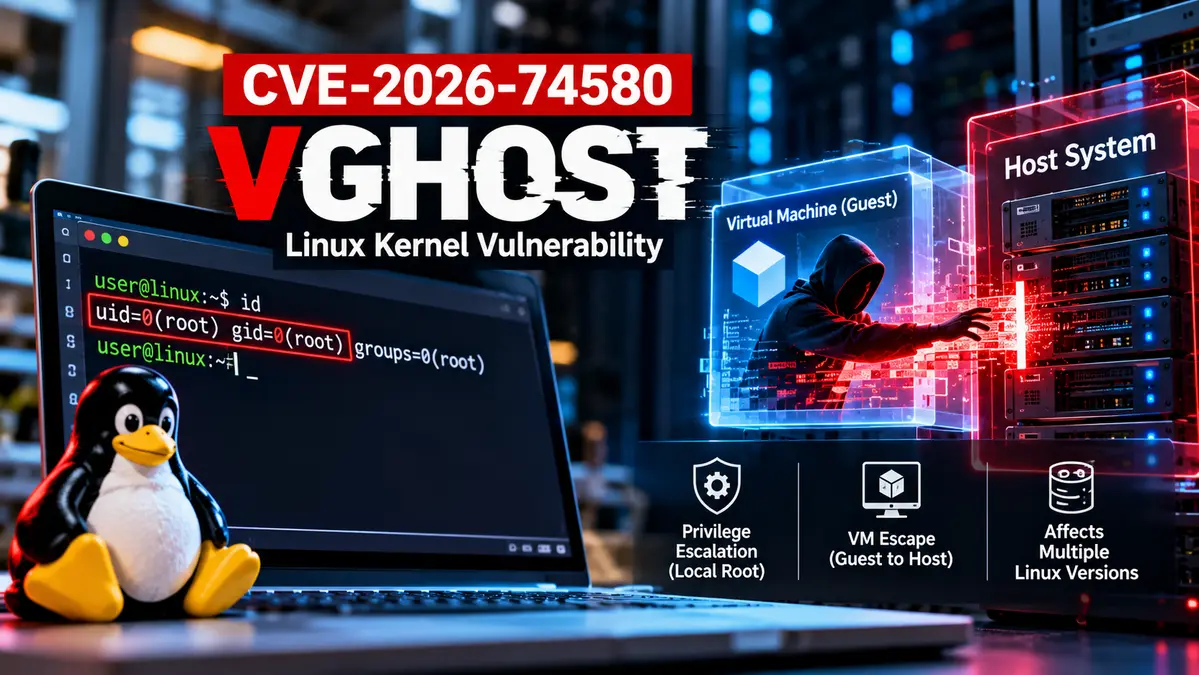
A Linux kernel flaw tracked as CVE-2026-74580 can allow a local user to gain root privileges and, in certain virtualization configurations, break out of a guest virtual machine and affect the host.
The vulnerability, named Vghost, affects the Linux vhost subsystem and was discovered by Tencent Zhuque Lab with assistance from its Corvus AI vulnerability-research system.
The flaw can provide an attacker with powerful read and write access to kernel memory, allowing privilege escalation from a low-privileged local account to root. In a narrower virtualization scenario, a malicious guest can also corrupt memory in the host’s QEMU process.
For broader coverage of major Linux and enterprise vulnerabilities, see our CVE and Vulnerability Exploits Security Hub.
Key Takeaway
CVE-2026-74580 is a high-severity Linux kernel vulnerability in the vhost subsystem that can allow local privilege escalation to root.
Researchers also demonstrated a guest-to-host attack path in specific virtualized configurations where a virtual IOMMU is enabled and vhost operates in device-IOTLB mode.
The vulnerability has been patched upstream, but administrators should verify that their distribution has shipped the fix and reboot into the updated kernel.
What Is CVE-2026-74580?
CVE-2026-74580 is a memory-handling vulnerability in Linux’s vhost subsystem.
vhost is used to accelerate virtualized I/O operations by moving some virtio processing into the Linux kernel.
The affected code maintains a metadata cache that stores previously validated memory mappings for virtual queues.
Researchers found that the cache was not properly reset when certain virtual-ring settings were changed while a queue was still active.
This could cause the kernel to keep using an outdated memory mapping even after the underlying ring address or size had changed.
Stale vhost Cache Leads to Out-of-Bounds Access
The vulnerability is rooted in how vhost tracks metadata mappings inside vq->meta_iotlb[].
A successful cache hit is treated as proof that a memory region was already validated.
However, when VHOST_SET_VRING_ADDR or VHOST_SET_VRING_NUM reconfigures a virtual ring, the cache was not always cleared.
That creates a stale mapping condition.
Once the stale entry is reused, vhost can translate an address using a memory region that no longer covers the requested location.
Subsequent read or write operations can then access memory outside the intended area.
Linux Kernel Flaw Can Give Local Users Root
The most direct impact of the vulnerability is local privilege escalation.
An attacker who can access the relevant vhost device node can manipulate the vulnerable interface and obtain arbitrary kernel-memory read and write capabilities.
That level of access can be used to bypass kernel protections, modify privileged data structures and escalate privileges to root.
Tencent researchers described the exploitation path as deterministic, meaning it does not depend on winning a race condition or repeatedly manipulating memory until an exploit succeeds.
Guest VM Can Also Reach the Host in Some Setups
Vghost also has a more serious virtualization impact in certain configurations.
If a virtual machine uses a virtio device behind a virtual IOMMU with iommu_platform enabled and vhost runs in device-IOTLB mode, the same flaw can be triggered from inside an untrusted guest.
In that scenario, the guest can cause the Linux host kernel to perform an out-of-bounds write into the host’s QEMU process memory.
Researchers demonstrated that this could be used to overwrite a function pointer and influence execution inside the host-side QEMU process.
This creates a path from a compromised or malicious guest VM toward the virtualization host.
This Is Not a Universal VM Escape
The guest-to-host impact requires specific virtualization settings and should not be described as a universal Linux VM escape.
The demonstrated path requires:
- A vulnerable Linux kernel
- A virtual machine using vhost
- A virtual IOMMU configuration
iommu_platformenabled- vhost operating in device-IOTLB mode
Systems without those conditions may still be vulnerable to the local privilege-escalation path if an attacker can reach the relevant vhost device.
Which Linux Versions Are Affected?
The flaw affects a broad range of Linux kernel versions.
The vulnerable behavior dates back to changes introduced around Linux 4.11 and later changes in Linux 5.9 that altered address validation behavior.
Researchers report that affected kernels extend through development versions of Linux 7.2 before the upstream fix was incorporated.
Because Linux distributions frequently backport security fixes, administrators should not rely only on the visible kernel version number.
The safest approach is to check the security advisory from the operating-system vendor.
Researchers Reproduced Root Access on Major Linux Distributions
Tencent Zhuque Lab reproduced the local root exploit on several widely used Linux platforms, including:
- Ubuntu 26.04
- Red Hat Enterprise Linux 9.8
- Amazon Linux 2023
- Microsoft Azure Linux 3.0
- Oracle Linux 10.2
The exact starting privileges differed between tested systems.
On some platforms, the relevant vhost device nodes were accessible to ordinary local users.
On Ubuntu, access was restricted to members of the kvm group, meaning an attacker needed membership in that group before reaching the vulnerable interface.
Why /dev/vhost-net and /dev/vhost-vsock Matter
Local attackers typically reach the vulnerable subsystem through device nodes such as:
/dev/vhost-net/dev/vhost-vsock
Permissions on these devices therefore have a significant effect on exploitability.
If they are world-accessible, any local user may potentially interact with the vulnerable interface.
If access is limited to a trusted virtualization group, the attack surface becomes narrower.
Upstream Linux Fix Resets the Metadata Cache
The Linux kernel fix changes vhost behavior so that the metadata cache is reset whenever the virtual ring is reconfigured.
This prevents stale mappings from being reused after ring addresses or sizes change.
The upstream fix is associated with commit:
de845981da67
Linux stable maintainers have backported the fix to supported kernel branches.
First Fixed Upstream Kernel Versions
According to published research, the first fixed versions in major upstream stable branches include:
- 5.10.265
- 5.15.216
- 6.1.183
- 6.6.152
- 6.12.104
- 6.18.45
- 7.1.9
- 7.2
Distribution kernels may include the patch under different version numbers because vendors frequently backport individual fixes.
Ubuntu Has Already Shipped Some Fixes
Ubuntu’s official CVE page rates CVE-2026-74580 as a high-severity issue with a CVSS score of 8.8.
Ubuntu has already published patched kernels for some supported releases and cloud-specific kernel packages.
However, Ubuntu’s advisory status can vary by release and kernel flavor.
Administrators should therefore check the official Ubuntu CVE tracker for the exact package used on their systems.
Severity Scores Differ Between Vendors
Security vendors do not all score CVE-2026-74580 identically.
Ubuntu and the Linux CVE ecosystem use a high-severity score of 8.8 in some assessments.
Other Linux vendors have assigned lower high-severity scores depending on how they evaluate privilege boundaries and the guest-to-host scenario.
This difference does not mean the vulnerability is disputed.
It reflects how different vendors interpret the CVSS scope and impact metrics for virtualization boundaries.
AI Helped Discover the Linux Kernel Flaw
One of the most notable aspects of Vghost is how it was found.
Tencent Zhuque Lab says the vulnerability was discovered with assistance from Corvus AI, its multi-agent vulnerability-research platform.
The Linux kernel patch itself credits the tooling through an Assisted-by attribution.
This is an example of AI-assisted vulnerability research rather than an AI system autonomously attacking Linux systems.
Human researchers still analyzed the finding, developed exploitation techniques, validated the impact and coordinated the fix.
Why AI-Assisted Kernel Research Matters
The Linux kernel contains millions of lines of highly complex code, including subsystems that have evolved for decades.
Memory-management and virtualization bugs can remain hidden for years because they may require a specific sequence of state changes before unsafe behavior becomes visible.
AI-assisted research systems can help researchers map relationships between code paths, identify suspicious assumptions and prioritize areas for manual review.
Vghost demonstrates how those tools may increasingly help uncover subtle security flaws in mature open-source software.
No Evidence of Active Exploitation
There is currently no public evidence that CVE-2026-74580 is being exploited in real-world attacks.
The vulnerability was disclosed through coordinated security research, and fixes were available before the full technical write-up became public.
However, detailed exploitation information is now available, increasing the importance of patching vulnerable systems.
How Linux Administrators Can Reduce Risk
The primary recommendation is to install a kernel containing the CVE-2026-74580 fix and reboot the system.
Administrators should also:
- Check their Linux vendor’s security advisory
- Verify the running kernel after installing updates
- Restrict access to
/dev/vhost-netand/dev/vhost-vsock - Remove unnecessary world-readable permissions
- Limit membership in virtualization-related groups such as
kvm - Audit multi-user and shared Linux hosts carefully
- Prioritize virtualization hosts that run untrusted or customer-controlled workloads
Temporary Mitigation for the Local Attack Path
If immediate patching is not possible, restricting access to vhost device nodes can reduce exposure to the local privilege-escalation path.
Administrators can review device permissions and ensure only trusted virtualization services or users can access them.
This should be treated as a temporary mitigation rather than a replacement for the patched kernel.
Guest-to-Host Path Requires the Kernel Fix
The virtualization escape scenario is more difficult to mitigate through simple permission changes because the attack originates from an already running guest configuration that legitimately interacts with vhost.
For environments matching the affected device-IOTLB configuration, installing the patched kernel is the recommended remedy.
Cloud and Hosting Providers Should Prioritize This Update
CVE-2026-74580 deserves particular attention in environments that host multiple users or virtual machines.
Examples include:
- Cloud infrastructure
- Virtual private server platforms
- Shared hosting
- Development environments
- CI/CD workers
- Research clusters
- Enterprise virtualization hosts
A privilege-escalation vulnerability becomes especially important when low-privileged users or untrusted workloads share the same underlying infrastructure.
Frequently Asked Questions
What is CVE-2026-74580?
CVE-2026-74580 is a Linux kernel vulnerability in the vhost subsystem that can allow out-of-bounds memory access and local privilege escalation.
What is Vghost?
Vghost is the name Tencent Zhuque Lab gave to CVE-2026-74580.
Can the vulnerability give an attacker root access?
Yes. Researchers demonstrated that a user with access to the affected vhost interface can obtain kernel-memory read and write capabilities and escalate to root.
Can Vghost escape a virtual machine?
In specific virtualization configurations, researchers demonstrated a guest-to-host attack path affecting the host’s QEMU process. This does not apply to every virtualized Linux deployment.
Is CVE-2026-74580 being actively exploited?
No public evidence of exploitation in the wild has been reported at the time of publication.
Was the vulnerability discovered by AI?
The vulnerability was discovered with assistance from Tencent Zhuque Lab’s Corvus AI system. Human researchers validated the flaw, developed the exploit and coordinated remediation.
How should administrators fix the issue?
Install the latest security kernel provided by the Linux distribution and reboot the system. Administrators should also verify permissions on vhost device nodes.
Final Takeaway
CVE-2026-74580, or Vghost, is a significant Linux kernel vulnerability because it combines reliable local privilege escalation with a potential guest-to-host path in certain virtualization environments.
The flaw is caused by stale metadata mappings in the vhost subsystem, allowing kernel reads and writes outside the intended memory region.
Tencent researchers demonstrated root access across several major Linux distributions and showed that specific virtualized environments can also expose the host-side QEMU process.
The Linux kernel fix is available, and administrators should update and reboot vulnerable systems rather than relying solely on temporary permission changes.
There is currently no evidence of active exploitation, but the availability of detailed technical research makes timely patching increasingly important.