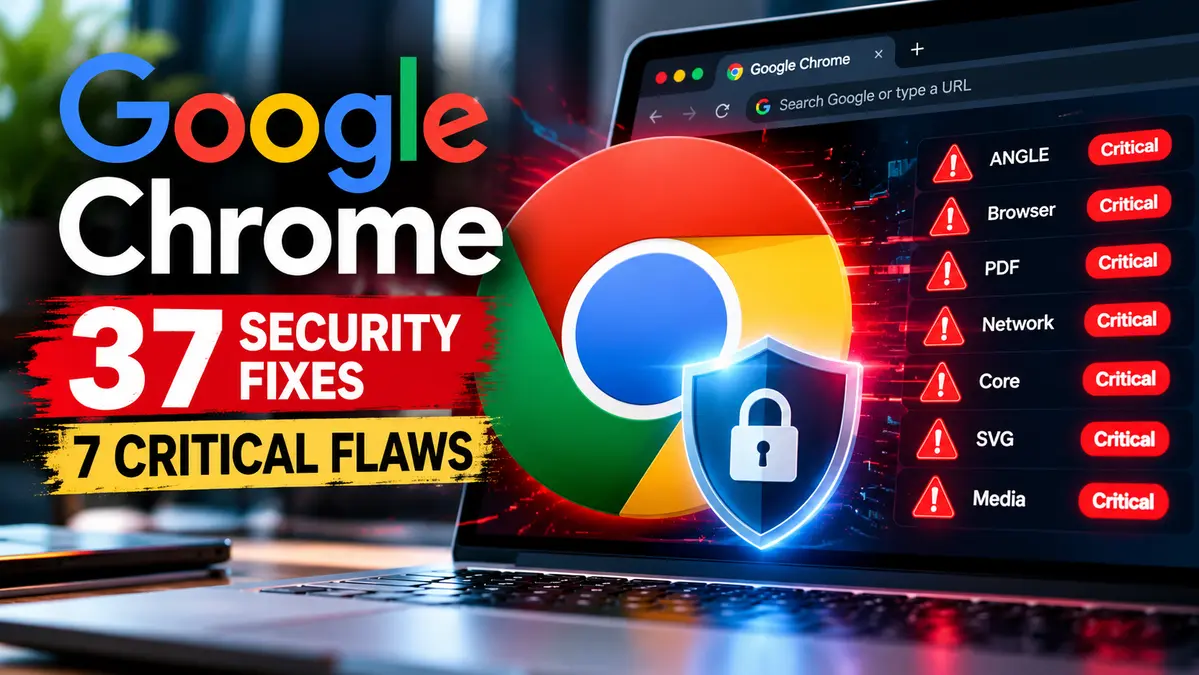
Google Chrome vulnerabilities fixed in the latest desktop update include 37 security issues, with seven rated critical and dozens of high-severity flaws affecting core browser components.
Google released the update on October 13, 2026 for Windows, macOS and Linux as part of the Stable Channel rollout.
The patched versions are 155.0.8059.79/.80 for Windows and Mac and 155.0.8059.79 for Linux.
According to Google’s official Chrome Stable Channel announcement, the release includes 37 security fixes and will continue rolling out over the coming days and weeks.
For broader coverage of high-impact software vulnerabilities and enterprise patching, see our CVE and Vulnerability Exploits Security Hub.
Key Takeaway
The latest Chrome security update fixes 37 vulnerabilities across graphics, PDF handling, networking, media, JavaScript execution, extensions and other browser subsystems.
Seven issues are rated critical, 29 are high severity and one is medium severity.
Google has not reported that the vulnerabilities are being actively exploited in the wild, but users should update promptly because several flaws involve memory corruption patterns that can potentially lead to code execution under suitable conditions.
Google Chrome Vulnerabilities Include 7 Critical Flaws
The seven critical vulnerabilities fixed in the October 13 update are:
- CVE-2026-110152 — Buffer overflow in ANGLE
- CVE-2026-110149 — Use after free in Browser
- CVE-2026-110136 — Use after free in PDF
- CVE-2026-110161 — Use after free in Network
- CVE-2026-110165 — Use after free in Core
- CVE-2026-110148 — Use after free in SVG
- CVE-2026-110151 — Use after free in Media
Most of the critical issues are use-after-free vulnerabilities, a class of memory-safety bug where software continues to access memory after that memory has already been released.
Depending on the affected component and exploitation conditions, such flaws can cause crashes, memory corruption or potentially allow malicious code execution.
CVE-2026-110152 Affects ANGLE Graphics Layer
CVE-2026-110152 is a critical buffer overflow affecting ANGLE, Chrome’s graphics translation layer.
The issue was reported by Zhenpeng “Leo” Lin at depthfirst on September 30, 2026.
A buffer overflow occurs when software writes more data than a memory region was designed to hold.
In security-sensitive components, this can corrupt nearby memory and potentially allow an attacker to influence program behavior.
Critical Use-After-Free Bugs Affect Core Browser Components
Six additional critical vulnerabilities involve use-after-free conditions.
These bugs affect:
- Chrome’s main Browser component
- PDF handling
- Networking
- Core browser logic
- SVG rendering
- Media processing
The wide component coverage means users can potentially encounter vulnerable code through different types of web content rather than through one isolated feature.
29 High-Severity Chrome Vulnerabilities Also Patched
The update also fixes 29 high-severity vulnerabilities.
A large number of these are memory-safety bugs, including use-after-free issues in:
- Desktop
- Bindings
- WebRTC
- Passwords
- Media
- V8
- DOM
- SVG
- Canvas
- ShapeDetection
Other high-severity issues include authorization weaknesses, information exposure, privilege elevation and buffer overflow conditions.
V8 JavaScript Engine Also Receives Security Fixes
Several vulnerabilities affect V8, the JavaScript and WebAssembly engine used by Chrome.
These include:
- CVE-2026-110140 — Type confusion in V8
- CVE-2026-110169 — Use after free in V8
- CVE-2026-110168 — Use after free in V8
JavaScript engine vulnerabilities are particularly important because untrusted web pages can interact directly with the engine during normal browsing.
However, successful exploitation of a V8 vulnerability inside the renderer does not automatically mean an attacker gains full control of the operating system.
Chrome’s sandbox is designed to limit what compromised renderer processes can access.
Code Execution Inside the Sandbox Is Not Full System Takeover
Some Chrome vulnerabilities can potentially allow arbitrary code execution inside the browser sandbox.
This distinction matters.
Code running inside Chrome’s renderer sandbox is still restricted from directly accessing many operating-system resources.
An attacker attempting full system compromise may need to combine a renderer vulnerability with another bug that escapes or bypasses the sandbox.
Therefore, phrases such as “one-click full computer takeover” should not be used unless Google or researchers specifically demonstrate such an exploit chain.
Chrome Password Components Receive Multiple Fixes
The October update also addresses several high-severity bugs related to password functionality.
These include:
- CVE-2026-110146 — Information leak in Passwords
- CVE-2026-110158 — Use after free in Passwords
- CVE-2026-110145 — Use after free in Passwords
Password-related browser components handle sensitive information and therefore receive additional scrutiny when security bugs are discovered.
Google has not publicly stated that passwords were stolen through these vulnerabilities in real-world attacks.
PDF and Media Components Also Affected
Google patched multiple vulnerabilities affecting Chrome’s PDF and media-processing code.
The PDF-related issues include:
- CVE-2026-110136 — Critical use after free in PDF
- CVE-2026-110147 — High-severity use after free in PDF
- CVE-2026-110155 — High-severity buffer overflow in PDFium
Media-processing bugs include several additional use-after-free issues and an observable discrepancy vulnerability.
These components regularly process untrusted files and web content, making memory-safety flaws particularly significant.
Extensions, Updater and Installer Bugs Also Fixed
The update is not limited to rendering and memory-corruption issues.
Google also fixed authorization and privilege-related flaws affecting Chrome’s Extensions, Updater and Installer components.
Examples include:
- CVE-2026-110156 — Incorrect reference resolution in Extensions
- CVE-2026-110159 — Incorrect authorization in Updater
- CVE-2026-110150 — Privilege elevation in Installer
These vulnerabilities highlight the breadth of the update, which touches both web-content processing and local browser-management functionality.
One Medium-Severity Vulnerability Included
The release also contains one medium-severity issue:
CVE-2026-110142, a use-after-free vulnerability affecting Chrome’s FileSystem component.
Google’s Stable Channel announcement lists this as the only medium-severity vulnerability in the 37-fix release.
Chrome 155.0.8059.79/.80 Contains the Fixes
Users should verify that Chrome has updated to one of the patched versions:
- Windows: 155.0.8059.79/.80
- macOS: 155.0.8059.79/.80
- Linux: 155.0.8059.79
Google says the update is rolling out progressively, so some devices may not receive it immediately.
How to Check Your Chrome Version
Chrome users can check for the update manually:
- Open Google Chrome
- Click the three-dot menu
- Select Help
- Open About Google Chrome
- Allow Chrome to check for and install updates
- Restart the browser when prompted
Users can also enter chrome://settings/help in the address bar to open the update page directly.
Enterprise Administrators Should Verify Deployment
Organizations managing large numbers of Chrome installations should verify that the new version has reached endpoints rather than assuming automatic updates completed successfully.
Recommended steps include:
- Confirm endpoint Chrome versions through device-management tools
- Prioritize internet-facing and high-risk workstations
- Restart Chrome after updates when required
- Review devices where automatic updates are disabled
- Check managed environments for version pinning
- Monitor Google Chrome security advisories for additional details
Google Is Temporarily Restricting Some Bug Details
Google says access to vulnerability details may remain restricted until a majority of users have installed the update.
This is a standard security practice intended to reduce the amount of technical information immediately available to attackers while vulnerable systems remain widespread.
Google may also continue restricting details when a vulnerability exists in a shared third-party library used by other projects that have not yet released fixes.
No Active Exploitation Announced
Google’s October 13 Chrome Stable Channel announcement does not state that any of the 37 vulnerabilities are being actively exploited in the wild.
That distinction is important.
A critical severity rating indicates the potential impact of a vulnerability, but it does not automatically mean attackers are currently exploiting it.
Users should still update promptly because disclosure of technical details can increase exploitation risk over time.
Chrome Has Received Multiple Large Security Updates This Month
The October 13 update follows another major Chrome 155 security release earlier in the month.
Google released Chrome 155.0.8059.39/.40 on October 6 with a much larger set of security fixes.
The latest release addresses a new batch of vulnerabilities and should be treated as a separate security update rather than assuming systems updated earlier in October remain fully protected.
Why Browser Updates Should Be Prioritized
Web browsers routinely process complex and potentially hostile content including:
- JavaScript
- Images
- Video and audio
- PDF documents
- Fonts
- WebRTC streams
- SVG graphics
- WebAssembly
A memory-safety flaw in one of those components can sometimes be triggered simply by processing attacker-controlled content.
Keeping browsers current therefore reduces exposure to vulnerabilities that attackers may attempt to weaponize through malicious or compromised websites.
Frequently Asked Questions
How many vulnerabilities did Google fix in Chrome?
Google’s October 13, 2026 Stable Channel update includes 37 security fixes.
How many critical Chrome vulnerabilities were patched?
Seven vulnerabilities are rated critical.
Which Chrome version fixes the vulnerabilities?
The patched versions are 155.0.8059.79/.80 for Windows and macOS and 155.0.8059.79 for Linux.
Are the Chrome vulnerabilities being actively exploited?
Google has not reported active exploitation of the 37 vulnerabilities in its October 13 Stable Channel announcement.
Can the vulnerabilities allow code execution?
Several memory-safety bugs can potentially lead to code execution depending on the affected component and exploitation conditions. However, code execution inside Chrome’s sandbox does not automatically mean full operating-system compromise.
What is the most serious vulnerability in the update?
The release includes seven critical vulnerabilities. Google has not publicly designated one of the seven as the single most severe flaw.
Should users update Chrome immediately?
Yes. Users should install the latest Chrome Stable update and restart the browser to ensure the patched version is running.
Final Takeaway
The latest Google Chrome security update fixes 37 vulnerabilities across some of the browser’s most important components.
Seven flaws are rated critical, including a buffer overflow in ANGLE and six use-after-free bugs affecting Browser, PDF, Network, Core, SVG and Media.
The update also fixes 29 high-severity vulnerabilities and one medium-severity FileSystem issue.
Google has not reported active exploitation, but users should update to Chrome 155.0.8059.79/.80 on Windows and macOS or 155.0.8059.79 on Linux as soon as the release becomes available.