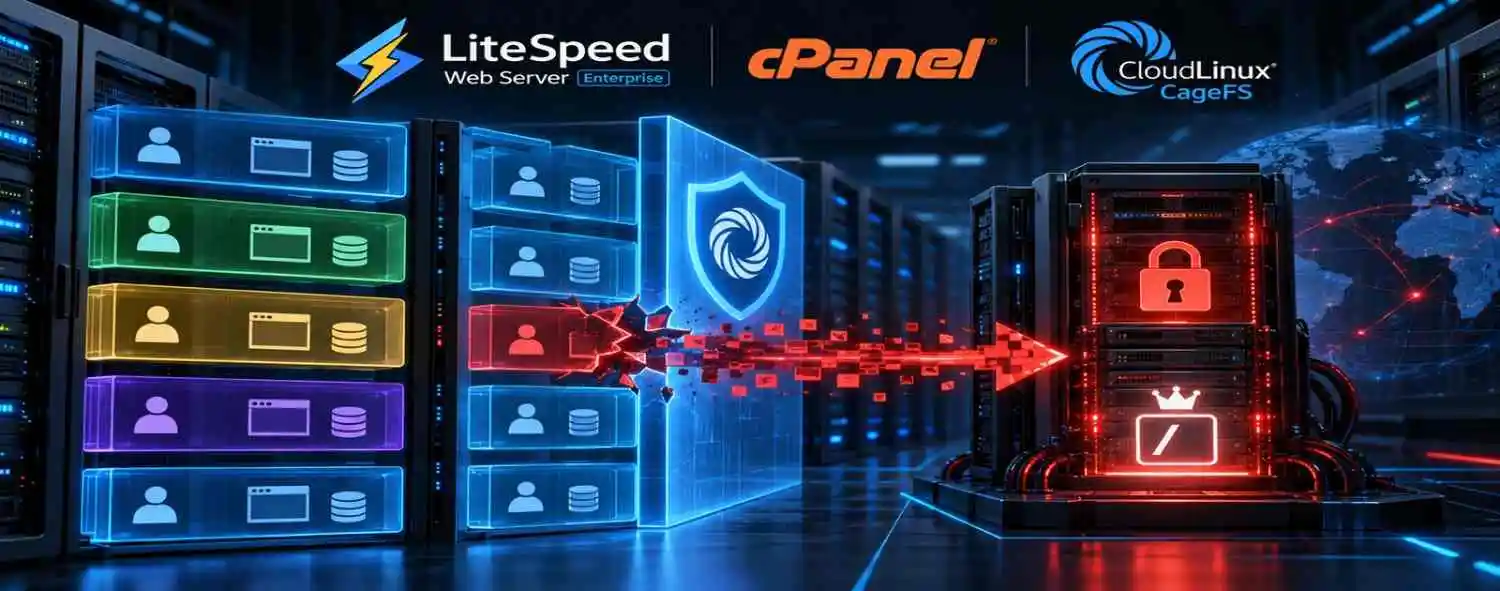
Executive Summary: A critical privilege-escalation vulnerability in LiteSpeed Web Server Enterprise could allow a low-privilege website account on a shared-hosting server to bypass isolation controls and potentially gain root-level access. cPanel says LiteSpeed Enterprise versions before 6.3.7 are affected and recommends upgrading to version 6.3.7 or later.
A critical privilege-escalation vulnerability in LiteSpeed Web Server Enterprise could allow a low-privilege website user on a shared-hosting server to gain root-level access, according to a security advisory published by cPanel on September 14, 2026.
The vulnerability affects LiteSpeed Web Server Enterprise versions earlier than 6.3.7. Because shared-hosting servers can run many customer websites on the same machine, a successful attack could potentially expose other hosted sites as well as the underlying server.
cPanel says the issue can also bypass account-isolation controls such as CloudLinux CageFS, potentially allowing a malicious hosting account to escape its restricted environment.
Administrators running LiteSpeed Enterprise should verify that affected servers have been upgraded to version 6.3.7 or later.
LiteSpeed Enterprise Versions Before 6.3.7 Are Affected
In its September 14 security advisory, cPanel described the issue as a critical privilege-escalation vulnerability affecting LiteSpeed Web Server Enterprise.
The affected range is straightforward:
- Affected: LiteSpeed Web Server Enterprise versions before 6.3.7
- Recommended version: LiteSpeed Web Server Enterprise 6.3.7 or later
The risk is particularly important for shared-hosting providers. Normally, one customer account should remain isolated from other customers and sensitive server-level resources.
According to cPanel, this vulnerability could break that security boundary and allow a malicious low-privilege website user to potentially reach root-level privileges.
Administrators following enterprise security issues can also check our Critical CVE Vulnerabilities 2026 Enterprise Security Hub for related vulnerability and patch coverage.
Why the CageFS Bypass Matters
One of the most serious parts of the advisory is the potential bypass of CageFS, an isolation technology commonly used with CloudLinux on shared-hosting servers.
CageFS provides each hosting user with a restricted filesystem environment. Its purpose is to prevent one account from freely viewing sensitive system files or data belonging to other customers.
cPanel says the LiteSpeed Enterprise vulnerability could allow a malicious website user to escape that restricted environment and potentially obtain root-level server access.
If exploitation succeeds, the attacker could potentially access or modify other websites hosted on the same machine as well as the underlying server.
Neither cPanel nor LiteSpeed has publicly disclosed the detailed exploitation chain, so the exact technical mechanism used to obtain root access should not be assumed.
LiteSpeed 6.3.7 Includes Security Improvements
LiteSpeed released LiteSpeed Web Server 6.3.7 on September 11, 2026, several days before cPanel publicly disclosed the vulnerability.
LiteSpeed described the release as containing security improvements, bug fixes and other changes.
The official LiteSpeed Web Server changelog lists multiple security-related changes for version 6.3.7.
- Enhanced
lscgidrequest authentication and validation. - Stronger validation of internal redirect URLs.
- Blocking important internal-use environment variables from being set through
.htaccess.
However, neither LiteSpeed nor cPanel has publicly identified which specific security change corresponds to the shared-hosting privilege-escalation vulnerability.
Until more technical details are released, it would be inaccurate to attribute the root-access issue to one particular LiteSpeed component.
How to Update LiteSpeed Enterprise to 6.3.7
cPanel strongly recommends upgrading affected LiteSpeed Enterprise installations to version 6.3.7 or later.
- Run command:
/usr/local/lsws/admin/misc/lsup.sh -f -v 6.3.7
The command is consistent with LiteSpeed’s official Web Server update documentation, which supports using lsup.sh to install a specified LiteSpeed version.
Administrators should verify the installed version after upgrading instead of assuming automatic updates have already deployed the security release.
Check the Installed LiteSpeed Version
- Check version:
cat /usr/local/lsws/VERSION - Check build:
cat /usr/local/lsws/BUILD
If the installed LiteSpeed Enterprise version is older than 6.3.7, the server falls within the affected range identified by cPanel.
Automatic Updates May Not Install 6.3.7 Immediately
LiteSpeed documentation explains that newly released versions may not immediately be pushed through the automatic Stable Tier update channel.
That means administrators should not assume an affected server has already received version 6.3.7 simply because automatic updates are enabled.
For hosting providers managing multiple LiteSpeed servers, checking the installed version across the entire server fleet is the safer approach.
Forced Updates Change Stable Tier Tracking
There is another operational detail administrators should understand before using the forced update command.
LiteSpeed documentation states that forcing a specific version with lsup.sh -f -v stops that installation from automatically following the Stable Tier.
Administrators who later want the server to resume following the Stable Tier can use LiteSpeed’s documented marker:
- Resume Stable Tier tracking:
touch /usr/local/lsws/autoupdate/follow_stable
This should be treated as an update-policy decision rather than blindly executed during remediation. Hosting providers with controlled patching procedures may intentionally manage versions differently.
No CVE Has Been Publicly Assigned Yet
As of September 15, the cPanel advisory does not provide a CVE identifier or CVSS score for this LiteSpeed Enterprise vulnerability.
The advisory also does not state that this specific vulnerability is being actively exploited in the wild.
Administrators should therefore avoid describing it as a zero-day or claiming active exploitation unless LiteSpeed, cPanel, CISA or another authoritative source publishes evidence supporting that claim.
The lack of a CVE does not reduce the significance of the issue. cPanel explicitly describes the vulnerability as critical and recommends upgrading affected systems.
No Public Exploit Details or Indicators of Compromise
Neither cPanel nor LiteSpeed has publicly explained exactly how the privilege escalation works.
The available vendor guidance also does not provide specific indicators of compromise for administrators trying to determine whether a server has previously been targeted through this vulnerability.
No separate workaround has been published for organizations that cannot immediately upgrade to 6.3.7.
For now, upgrading affected LiteSpeed Enterprise installations remains the primary documented remediation.
Is OpenLiteSpeed Affected?
The cPanel security advisory specifically identifies LiteSpeed Web Server Enterprise as the affected product.
It does not state that OpenLiteSpeed is affected.
Because the technical root cause has not been disclosed, administrators should not assume that the same vulnerability exists in OpenLiteSpeed.
OpenLiteSpeed impact should remain classified as unknown unless LiteSpeed publishes separate guidance.
Not the First LiteSpeed Root-Access Issue This Year
This marks the third time since May 2026 that a LiteSpeed-related flaw on cPanel servers has been reported to potentially give a hosting account root-level access, but it is the first of these incidents tied directly to LiteSpeed Web Server Enterprise rather than the user-end cPanel plugin.
In May and June, LiteSpeed disclosed two privilege-escalation vulnerabilities in its user-end cPanel plugin: CVE-2026-48172 and CVE-2026-54420. LiteSpeed said both vulnerabilities were being actively exploited, and CISA later added them to its Known Exploited Vulnerabilities catalog.
Those earlier flaws were patched in the plugin. The newly disclosed September issue is separate because cPanel identifies LiteSpeed Web Server Enterprise itself as the affected product.
That distinction matters for administrators because this Enterprise vulnerability requires its own remediation and should not be treated as already resolved simply because the earlier cPanel plugin flaws were patched.
Why Shared Hosting Providers Should Prioritize the Update
The biggest concern is not simply privilege escalation inside a single website account. It is the possibility of crossing the isolation boundary of a multi-tenant hosting server.
A shared server can host dozens or even hundreds of customer websites. If one compromised account can potentially reach root, the blast radius may extend far beyond the original website.
This makes the issue particularly important for hosting companies, cPanel administrators, managed hosting providers and organizations operating large multi-tenant LiteSpeed environments.
The security concept is similar to other isolation-boundary failures. CyberUpdates365 previously covered a VMware ESXi sandbox escape vulnerability, although that vulnerability affects a completely different platform and is not technically related to this LiteSpeed issue.
What Administrators Should Do Now
Administrators responsible for LiteSpeed Enterprise servers should identify affected installations and prioritize the security update.
- Check the LiteSpeed Web Server version running on each server.
- Identify Enterprise installations running versions earlier than 6.3.7.
- Upgrade affected systems to LiteSpeed Web Server Enterprise 6.3.7 or later.
- Verify the installed version and build after upgrading.
- Review whether the forced update changed Stable Tier tracking behavior.
- Monitor LiteSpeed and cPanel advisories for CVE assignment, exploitation details or additional detection guidance.
CyberUpdates365 Analysis
This vulnerability deserves attention because shared hosting depends heavily on effective tenant isolation.
The broader 2026 pattern is also worth noting. LiteSpeed-related components have now been involved in multiple root-level privilege-escalation disclosures on cPanel environments within a few months. Although the September Enterprise flaw is technically distinct from the earlier plugin vulnerabilities, the repeated appearance of root-level privilege-escalation issues in LiteSpeed-related cPanel environments makes disciplined patching and version verification especially important for hosting providers.
If one low-privilege hosting account can break that boundary and potentially gain root access, the impact can expand from a single compromised website to the wider hosting server.
There is still limited public technical information about the vulnerability. No CVE, CVSS score, detailed exploitation mechanism or confirmed active-exploitation status has been published in cPanel’s advisory.
For that reason, speculation about the underlying root cause should be avoided.
The confirmed response is straightforward: LiteSpeed Enterprise installations running versions before 6.3.7 should be identified and upgraded as soon as operationally practical.
Official Sources
- cPanel LiteSpeed Enterprise Security Advisory
- LiteSpeed Web Server 6.3.7 Release Announcement
- LiteSpeed Web Server Changelog
- LiteSpeed Web Server Update Documentation