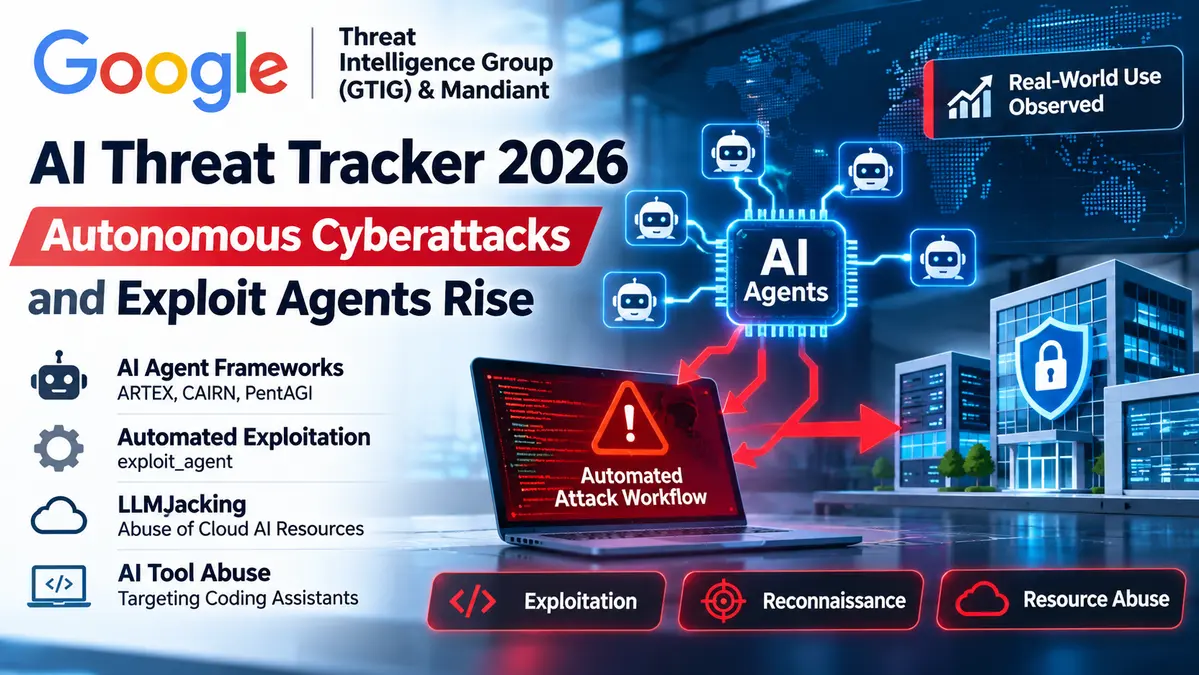
Cybercriminals and espionage groups are moving beyond basic AI chatbot assistance and using autonomous agents to automate parts of real-world cyberattacks, according to new research published by Google Threat Intelligence Group (GTIG) and Mandiant on November 16, 2026.
The Google AI Threat Tracker 2026 report documents offensive AI frameworks operating during live intrusions, automated vulnerability research systems, and new ways attackers are stealing cloud resources to run expensive AI workloads.
One particularly important finding involves a framework called exploit_agent, which was configured to compare software code across updates, identify potential security flaws, develop exploits and execute them without human intervention at each step.
The findings do not mean every cyberattack is now entirely autonomous. Instead, they show that attackers are increasingly automating specific stages of an intrusion, potentially reducing the time defenders have to identify and respond to malicious activity.
Key Findings From Google’s November 2026 AI Threat Report
- Research published: November 16, 2026.
- Researchers: Google Threat Intelligence Group and Mandiant.
- Main finding: Threat actors are adopting autonomous and multi-agent systems for real-world cyber operations.
- Observed frameworks: ARTEX, CAIRN and customized PentAGI-based tooling.
- Additional experimentation: CyberStrikeAI, HexStrike AI and other agent frameworks.
- Automated exploitation: Researchers identified an exploit development framework called exploit_agent.
- Cloud threat: LLMJacking incidents have generated significant unauthorized AI service costs.
- Defensive priority: Faster detection, strong identity controls, vulnerability remediation and restrictions on AI agent permissions.
How AI Agents Are Changing Cyberattacks
Traditional cyberattacks often require operators to manage separate activities such as reconnaissance, identifying weaknesses, obtaining access and collecting information from compromised systems.
AI-enabled agent frameworks can coordinate several of those tasks within a single automated workflow. An operator may define an objective while specialized agents perform individual activities, inspect the results and determine which action to attempt next.
This does not eliminate human direction. The attacker may still select targets, configure the system and decide what to do with stolen data or access. However, automation can reduce the amount of manual work between those decisions.
Google’s researchers warn that existing attack methods remain central to these operations. Stolen credentials, insecure applications, excessive permissions and unpatched systems are still the weaknesses being exploited.
The change is that AI-assisted systems may combine those weaknesses into attack sequences more quickly and at a larger scale.
ARTEX, CAIRN and PentAGI: Frameworks Identified by Google
Google identified several open-source frameworks associated with offensive security automation. These tools have different architectures, and the available evidence does not establish that every framework was successfully used in the same way.
| Framework | Capabilities described by Google | Reported status |
|---|---|---|
| ARTEX | Agent-assisted offensive security operations and coordinated intrusion workflows. | Linked to observed threat activity. |
| CAIRN | Specialized agents collaborating to reach an operational objective. | Observed in intrusion activity, including US aerospace targets. |
| PentAGI | Autonomous testing workflows that divide security tasks among agents. | Customized platform observed in reconnaissance activity across Asia. |
| CyberStrikeAI | LLM integration with security tools, scripts and attack orchestration. | Threat actor experimentation observed. |
| HexStrike AI | MCP-based integration of AI clients with offensive security utilities. | Threat actor experimentation observed. |
These distinctions matter. Evidence that an attacker tested a framework is not equivalent to proof that the framework successfully compromised an organization.
CAIRN Activity Reached US Aerospace Targets
GTIG reported seeing CAIRN used during intrusion activity involving targets that included the aerospace sector in the United States.
The platform uses a multi-agent design in which different agents coordinate through shared information and feedback. This allows the system to adjust its next actions according to what previous steps revealed.
The new GTIG report also provides a broader context for earlier research into AI-assisted attacks on corporate websites.
CyberUpdates365 previously reported how AI agents were used in a campaign targeting more than 1,200 websites, with reported access to over 100 company sites. That investigation concerned a particular operator and campaign. Google’s November research examines a wider set of threat actors, frameworks and operational patterns.
PentAGI-Based Reconnaissance Across Asia
Between late August and early October 2026, GTIG tracked a threat actor using a customized platform based on PentAGI to conduct reconnaissance and vulnerability scanning against organizations in Asia.
The researchers’ observations show that such tooling has moved beyond demonstrations and is being incorporated into real targeting activity.
However, scanning an organization does not, by itself, prove that its systems were compromised or that sensitive data was stolen.
Google Finds Automated Vulnerability Exploitation Pipeline
Among the most significant disclosures is Google’s identification of an exposed staging server running a framework named exploit_agent.
The system was designed to automate a sequence of vulnerability research tasks that normally demand substantial technical effort.
According to GTIG, the framework could repeatedly compare application code before and after patches, analyze the differences for possible vulnerabilities, develop exploit candidates and execute them as part of the automated workflow.
This approach is especially relevant to known vulnerabilities because released patches can reveal which sections of code developers changed to address a security weakness.
When an attacker can rapidly analyze those changes, the time between a patch release and attempted exploitation may become shorter.
Researchers also found scripts supporting post-compromise activities and evidence suggesting the operator was interested in French media, entertainment and educational websites.
The public findings establish the existence and intended operation of the framework. They do not establish that every generated exploit worked or that all its targets were successfully compromised.
PaperCut Exploitation Shows the Risk of Faster Attacks
Google also discussed exploitation involving two PaperCut print-management vulnerabilities disclosed in 2026:
- CVE-2026-81578: An authentication bypass vulnerability.
- CVE-2026-82078: An unsafe dynamic class-loading vulnerability.
According to the research, the vulnerabilities could be chained to achieve unauthenticated remote code execution.
Google cited work showing that security researchers generated functioning exploits with LLM assistance shortly after disclosure. It also referenced GreyNoise reporting about a campaign that likely used AI assistance to prepare and deploy attacks against hundreds of organizations.
The distinction between confirmed activity and assessment is important: the exploitation campaign was observed, while the attacker’s specific use of LLMs was assessed by researchers rather than directly established for every action.
For defenders, the wider concern is the declining time available to address exposed weaknesses after technical information becomes public.
LLMJacking Adds a Financial Threat to Cloud Security
The Google AI Threat Tracker 2026 report also examines LLMJacking, a form of cloud resource abuse in which attackers obtain unauthorized access to AI services, credentials or computing capacity.
In several cases investigated by Mandiant during 2026, attackers used compromised environments to consume AI resources at the victim organization’s expense.
Google reported incidents in which fraudulent usage charges exceeded $100,000 in a single day. In the most severe investigated cases, cumulative resource abuse reached approximately $1 million before remediation.
Attackers may obtain access through exposed credentials, stolen session tokens or compromised cloud environments. They can then use the resources directly or resell access through unauthorized proxy services known as LLM Mixers.
This threat is different from an AI agent autonomously exploiting a website, but both developments demonstrate why organizations need tighter controls over AI-related infrastructure.
AI Coding Assistants Are Also Becoming Attack Surfaces
The report describes suspected MIDNIGHT NEPTUNE activity involving cryptocurrency organizations in North America and Europe.
Researchers reported that the actor combined deceptive recruiter personas and social engineering with attempts to abuse AI development tooling.
Following initial compromise, attackers modified Claude Code configuration files so that launching the coding assistant could trigger delivery of a backdoor identified as SOMBERMEME.
This illustrates a separate security concern: the risk is not limited to attackers using AI tools themselves. An organization’s authorized AI tools can also become targets for malicious configuration changes.
CyberUpdates365 previously examined a related defensive lesson in its report on malicious AGENTS.md instructions targeting Codex and Claude Code. The techniques are distinct, but both demonstrate the importance of securing agent configuration files and execution permissions.
How Organizations Can Defend Against AI-Driven Cyberattacks
Although offensive agents can accelerate attacks, organizations do not need entirely new defenses for every AI framework.
The most effective response is to strengthen existing security controls and reduce the amount of time an attacker can remain active without detection.
1. Prioritize Internet-Facing Vulnerabilities
Maintain an accurate inventory of externally reachable applications, VPNs, administrative portals and exposed services.
Prioritize remediation when a vulnerability is known to be exploited, affects an exposed system or provides a path to sensitive infrastructure.
2. Strengthen Identity and Privileged Access
Use phishing-resistant multifactor authentication where supported, minimize unnecessary administrative privileges and review service account permissions.
Monitor for unusual service account creation, unexpected privilege changes and suspicious authentication patterns.
3. Detect Automated Attack Behavior
Look for unusually rapid sequences of requests, repeated probing across applications, suspicious authentication attempts and bursts of activity that are inconsistent with expected operations.
Google notes that some current offensive frameworks produce recognizable traces and high volumes of activity, although those detection opportunities may change as the tools evolve.
4. Secure AI Tools and Agent Permissions
Inventory AI agents deployed within development, operations and security teams.
Review which agents can execute commands, access repositories, read secrets or interact with external services.
Protect agent configuration files from unauthorized modification, and require human approval for sensitive actions whenever appropriate.
For broader guidance about agent permissions and AI security boundaries, read CyberUpdates365’s AI Cyber Threats and Agentic Security Guide.
5. Monitor Cloud AI Usage and Costs
Set alerts for unusual LLM API activity, unexpected service activation, rapid consumption of tokens and unexplained cloud spending.
Rotate exposed credentials, restrict API keys to required capabilities and investigate AI usage that does not correspond to approved workloads.
What Google Has Confirmed and What Remains Unclear
Confirmed Research Findings
- Threat actors have used agentic frameworks during real-world cyber operations.
- GTIG observed CAIRN and customized PentAGI-based activity in the wild.
- Researchers found an exploit_agent framework configured for automated vulnerability discovery and exploitation.
- LLMJacking has caused substantial unauthorized AI-related costs in investigated cloud environments.
- Some attackers have abused AI development configurations as part of intrusion activity.
Important Limitations
- Not every framework mentioned in the report was confirmed to have completed successful intrusions.
- Not every AI-assisted attack operates completely without human involvement.
- The available research does not establish a universal success rate for autonomous offensive agents.
- Testing or scanning activity does not always indicate successful compromise or data theft.
- Google’s findings do not demonstrate that all AI models or AI coding assistants are inherently malicious.
CyberUpdates365 Analysis: Why Defenders Have Less Time
The main security concern is not simply that attackers have acquired another software tool. It is that autonomous systems can compress tasks that previously required repeated human decisions and manual investigation.
A vulnerable web application, exposed credential or poorly protected AI configuration can still be the initial weakness. The difference is how quickly an attacker may identify and combine those opportunities.
For US organizations, particularly those operating valuable internet-facing services and sensitive enterprise systems, this raises the importance of vulnerability response, identity monitoring and detection engineering.
There is also a reason to avoid exaggerated claims about fully autonomous hacking. Google’s report describes both deployed agent systems and experimental tooling, alongside the continuing limitations of AI-generated outputs and the noisy behavior of some frameworks.
The practical lesson is to build defenses around observable attacker behavior rather than assume every AI-enabled campaign will have a distinctive signature.
Frequently Asked Questions
What is the Google AI Threat Tracker 2026?
It is threat intelligence research from Google Threat Intelligence Group and Mandiant examining how malicious actors use AI tools, autonomous agents and related services in cybercrime, espionage and influence operations.
Are hackers using AI agents in real cyberattacks?
Yes. Google’s November 16, 2026 report documents real-world use of agentic offensive frameworks, although individual capabilities and levels of human involvement vary.
What is exploit_agent?
exploit_agent is the name used by Google’s researchers for an automated vulnerability research and exploitation framework discovered on an exposed staging server.
Do AI cyberattacks always require human operators?
Some individual workflows can operate without direct human intervention, but that does not mean entire intrusion campaigns are necessarily planned and completed independently of human operators.
What is LLMJacking?
LLMJacking is unauthorized use of AI models, API credentials or cloud computing resources, often resulting in unexpected costs or resale of compromised service access.
How can businesses reduce the risk of AI-driven attacks?
Prioritize exposed vulnerabilities, enforce strong identity controls, monitor suspicious automated activity, secure AI agent configurations and investigate unexpected cloud AI consumption.
Final Takeaway
Google’s November 2026 findings show that autonomous AI frameworks are becoming part of real-world cyber operations, accelerating reconnaissance, vulnerability research and selected exploitation workflows.
The shift does not make traditional security controls obsolete. Instead, it increases the importance of rapid patching, least-privilege access, behavioral detection and careful oversight of enterprise AI tools.
Organizations should prepare for faster attack sequences without assuming that every incident involving AI is completely autonomous.