Citrix NetScaler RCE vulnerability CVE-2026-107406 is a newly disclosed critical flaw affecting NetScaler ADC and NetScaler Gateway appliances under specific SAML configurations.
The memory overflow vulnerability can lead to remote code execution or denial of service and carries a CVSS v4.0 score of 9.5.
Citrix published security bulletin CTX697191 on October 8, 2026 and strongly urged affected customers to upgrade to fixed builds as soon as possible.
At the time of publication, Citrix said it was not aware of any unmitigated exploits targeting this vulnerability.
For broader coverage of high-risk enterprise vulnerabilities, see our CVE and Vulnerability Exploits Security Hub.
Key takeaway: CVE-2026-107406 does not affect every NetScaler deployment. Exposure depends on both the installed version and whether the appliance is configured as a SAML service provider or identity provider.
What Is CVE-2026-107406?
CVE-2026-107406 is a memory overflow vulnerability in Citrix NetScaler ADC and NetScaler Gateway.
Citrix classifies the flaw under CWE-119, which covers improper restriction of operations within the bounds of a memory buffer.
Successful exploitation can cause:
- Remote code execution
- Denial of service
- Loss of confidentiality
- Loss of integrity
- Loss of availability
The published CVSS vector indicates that exploitation can occur over the network without authentication or user interaction, although Citrix rates attack complexity as high.
Which NetScaler Systems Are Affected?
The vulnerability only applies when the appliance is configured for certain SAML roles and the installed build falls within Citrix’s affected ranges.
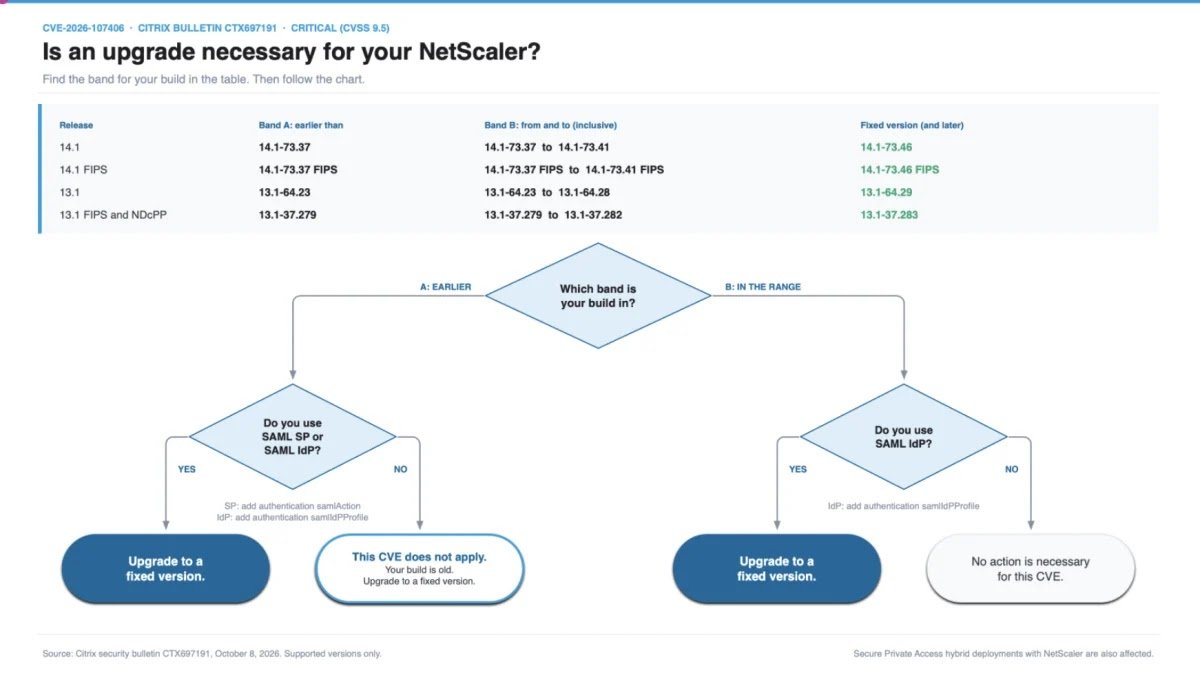
- The vulnerability only applies when the appliance is configured for certain SAML roles.
- Citrix separates affected versions into two groups.
Versions Affected When Configured as SAML IdP
- NetScaler ADC and NetScaler Gateway 14.1-73.37 through 14.1-73.41
- NetScaler ADC 14.1-FIPS 14.1-73.37 FIPS through 14.1-73.41 FIPS
- NetScaler ADC and NetScaler Gateway 13.1-64.23 through 13.1-64.28
- NetScaler ADC 13.1-FIPS and NDcPP 13.1-37.279 through 13.1-37.282
Older Versions Affected When Configured as SAML SP or SAML IdP
- NetScaler ADC and NetScaler Gateway before 14.1-73.37
- NetScaler ADC 14.1-FIPS before 14.1-73.37 FIPS
- NetScaler ADC and NetScaler Gateway before 13.1-64.23
- NetScaler ADC 13.1-FIPS and NDcPP before 13.1-37.279
This version-specific distinction is important because simply having SAML enabled does not automatically mean every appliance is vulnerable.
How to Check Whether Your Appliance Meets the Preconditions
Administrators can inspect NetScaler configuration entries to determine whether an appliance is acting as a SAML service provider or identity provider.
Citrix lists the following indicators:
SAML Service Provider:
add authentication samlActionSAML Identity Provider:
add authentication samlIdPProfileThese entries must then be compared against the affected version ranges.
Finding one of these settings alone is not enough to determine vulnerability status without checking the installed build.
Fixed Citrix NetScaler Versions
Citrix strongly recommends upgrading affected deployments to the following releases or later:
- NetScaler ADC and Gateway 14.1: 14.1-73.46 or later
- NetScaler ADC and Gateway 13.1: 13.1-64.29 or later
- NetScaler ADC 14.1-FIPS: 14.1-73.46 FIPS or later
- NetScaler ADC 13.1-FIPS / NDcPP: 13.1-37.283 or later
Administrators should use these builds as the remediation baseline for CVE-2026-107406 rather than relying on patches deployed for earlier NetScaler vulnerabilities.
Why Earlier NetScaler Patches May Not Be Enough
NetScaler appliances have received multiple security updates during 2026.
An appliance that was patched for a previous vulnerability may still remain exposed to CVE-2026-107406 if it has not been upgraded to one of the newly fixed builds.
Security teams should therefore verify the exact software version rather than assuming an appliance is protected because a recent NetScaler patch was already installed.
Secure Private Access Hybrid Deployments Are Also Affected
Citrix says Secure Private Access Hybrid deployments using affected NetScaler instances are also impacted.
Those instances must be upgraded to the recommended builds.
The bulletin applies specifically to customer-managed NetScaler ADC and NetScaler Gateway appliances.
Citrix-managed cloud services and Citrix-managed Adaptive Authentication are updated directly by the vendor.
Is CVE-2026-107406 Being Exploited?
Citrix said that, as of the bulletin’s publication, it was not aware of any unmitigated exploits of CVE-2026-107406.
That statement should not be interpreted as proof that every deployment is safe.
NetScaler appliances are commonly deployed at the network edge and often provide remote access, authentication and traffic-management functions.
Organizations should therefore prioritize remediation before proof-of-concept exploit code or active exploitation emerges.
Why NetScaler RCE Vulnerabilities Are High Risk
NetScaler ADC and Gateway appliances frequently sit directly on the internet-facing perimeter.
Depending on deployment, they can handle:
- SSL VPN access
- Authentication flows
- SAML single sign-on
- Application delivery
- Traffic management
- Remote workforce connectivity
A remote code execution vulnerability in an edge appliance can provide attackers with a valuable foothold before they ever reach internal systems.
What Security Teams Should Do Now
Organizations using Citrix NetScaler should take immediate inventory and verification steps.
- Identify all customer-managed NetScaler ADC and Gateway appliances.
- Record the installed build version for each appliance.
- Check whether SAML SP or SAML IdP configurations are present.
- Compare the configuration and version against Citrix’s affected ranges.
- Upgrade vulnerable appliances to the recommended fixed build.
- Review authentication, system and network logs for suspicious activity.
- Confirm that previously patched appliances also meet the new build requirements.
Why SAML Configuration Matters
SAML is widely used for enterprise single sign-on.
In a typical deployment:
- A SAML identity provider authenticates users and issues identity assertions.
- A SAML service provider accepts those assertions and grants access to an application or service.
CVE-2026-107406 is tied to these SAML-related configurations, but the exact affected role changes depending on the NetScaler build.
This is why administrators must check both configuration and version.
No Public Exploit Details in Citrix Bulletin
Citrix has not published technical exploit instructions or proof-of-concept code in its security bulletin.
The company describes the issue as a memory overflow capable of causing remote code execution or denial of service under the documented configuration conditions.
Security teams should avoid waiting for public exploit details before patching.
Researchers Credited for the Discovery
Citrix credited several researchers for helping identify and report the vulnerability:
- Michael Tucker — JPMorgan Chase XOR Team
- Chew Keong Tan — JPMorgan Chase XOR Team
- Alex Bernier — JPMorgan Chase XOR Team
- Maxim Suhanov
Citrix did not associate the vulnerability with a specific threat actor, victim organization or attack campaign in its bulletin.
Frequently Asked Questions
What is CVE-2026-107406?
CVE-2026-107406 is a critical memory overflow vulnerability affecting certain SAML-configured Citrix NetScaler ADC and NetScaler Gateway deployments.
What can an attacker do with the vulnerability?
Citrix says successful exploitation may lead to remote code execution or denial of service.
What is the CVSS score?
The vulnerability has a CVSS v4.0 base score of 9.5 and is rated Critical.
Does the vulnerability affect every NetScaler appliance?
No. Exposure depends on both software version and whether the appliance is configured as a SAML service provider or identity provider.
Which versions contain the fix?
Citrix recommends 14.1-73.46 or later, 13.1-64.29 or later, 14.1-73.46 FIPS or later, and 13.1-37.283 or later for applicable FIPS and NDcPP branches.
Is the vulnerability being actively exploited?
Citrix said it was not aware of any unmitigated exploits when the security bulletin was published.
Are Citrix-managed cloud services affected?
The bulletin applies to customer-managed NetScaler instances. Citrix-managed cloud services and Adaptive Authentication are upgraded by Citrix.
How can administrators check for SAML configuration?
Administrators can search the NetScaler configuration for add authentication samlAction or add authentication samlIdPProfile, then compare the deployment’s version with Citrix’s affected build ranges.
Final Takeaway
The critical Citrix NetScaler RCE vulnerability CVE-2026-107406 should be treated as a priority for organizations using SAML-enabled NetScaler ADC and Gateway appliances.
The flaw can lead to remote code execution or denial of service, but exposure is dependent on specific SAML roles and software versions.
Citrix has already released fixed builds and is urging affected customers to upgrade immediately.
Organizations should verify every NetScaler appliance individually rather than assuming previous security updates already address this new vulnerability.
Stay Updated on Critical Vulnerabilities
Internet-facing appliances remain frequent targets for attackers because they often sit directly between external users and sensitive enterprise systems.
Follow CyberUpdates365 for verified vulnerability alerts, patch guidance, enterprise security updates and practical remediation advice.
Official Sources
Citrix Security Bulletin CTX697191:
Citrix NetScaler ADC and Gateway Security Bulletin for CVE-2026-107406
Citrix Security Guidance:
Immediate Guidance for CVE-2026-107406