Brazilian cyber threat actors have weaponized advanced image manipulation techniques against enterprise networks. Cybersecurity intelligence confirms that Caminho malware LSB steganography operations actively conceal malicious .NET assemblies inside ordinary image files, delivering persistent remote access tools to corporate workstations across South America, Africa, and Eastern Europe.
Active since early 2025, the Caminho loader represents an escalating operational risk. Instead of relying on traditional file droppers that trigger immediate antivirus signatures, the threat syndicate exploits legitimate cloud repositories and Least Significant Bit (LSB) image pixel manipulation. Understanding how Caminho malware LSB steganography bypasses perimeter security requires analyzing its multi-stage infection chain and memory-only execution model.
How Caminho Malware Uses LSB Steganography to Hide .NET Payloads
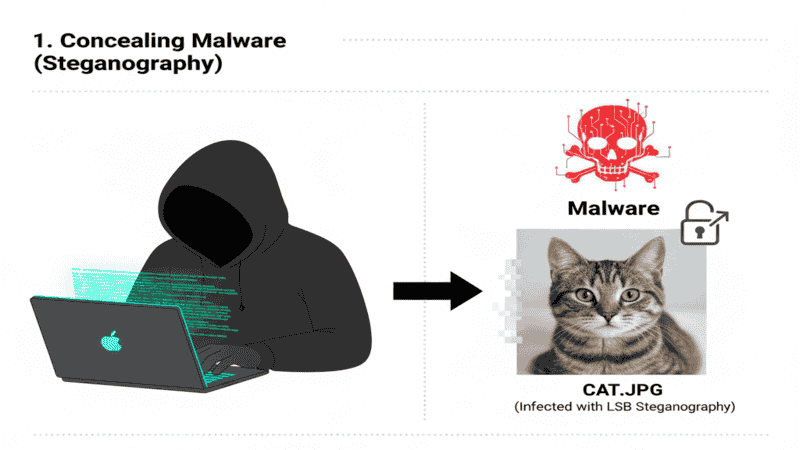
The core innovation behind the Caminho loader lies in its use of Least Significant Bit (LSB) steganography to conceal compiled .NET assemblies within seemingly harmless JPG and PNG graphic assets.
The infection chain begins when a victim receives a spear-phishing email disguised as an urgent commercial quotation or unpaid invoice. The attached archive extracts a lightweight JavaScript or VBScript dropper. Upon execution, the script fetches an obfuscated PowerShell loader from public paste repositories, which subsequently pulls a steganographic image file from legitimate archival platforms such as archive.org.
Once downloaded, the PowerShell routine analyzes the raw byte stream of the graphic. It searches for specific image header markers, iterates through pixel coordinates, and extracts RGB color channel values where malicious code is embedded across the least significant bits. The first four extracted bytes declare the payload length, followed by a Base64-encoded executable assembly.
| Attack Component | Traditional Malware Approach | Caminho Loader Methodology | Defensive Challenge |
|---|---|---|---|
| Payload Hosting | Known malicious bulletproof domains | Legitimate archive.org repositories | Domain reputation filters fail |
| File Inspection | Direct executable (.exe / .dll) attachment | Steganographic JPG / PNG images | Static antivirus detects no malware |
| Execution Model | Disk write to AppData / Temp directories | In-memory reflection and process hollowing | Zero persistent file artifacts on disk |
| Persistence | Registry Run keys | Scheduled tasks targeting legitimate binaries | Runs every 60 seconds via calc.exe |
Multi-Stage Malware Delivery: RATs and Infostealers
The infrastructure underlying Caminho malware LSB steganography campaigns operates under a Loader-as-a-Service business model. Multiple cybercriminal syndicates contract the delivery platform to deploy diverse malicious families depending on the victim’s industry:
- REMCOS Remote Access Trojan (RAT): Provides operators with comprehensive remote command execution, microphone surveillance, and webcam hijacking.
- XWorm Modular Malware: Enables unauthorized network propagation, distributed denial-of-service (DDoS) capabilities, and automated data exfiltration.
- Katz Stealer: Systematically harvests stored browser passwords, session cookies, cryptocurrency wallet keys, and enterprise VPN tokens.
To monitor active zero-day exploits and evasion mechanisms utilized by international threat actors, explore our 2026 Enterprise CVE & Vulnerabilities Security Hub.
Actionable Verification Commands for Incident Responders
Because Caminho malware executes entirely in memory and injects payloads into legitimate Windows processes like calc.exe, security operations teams must use live behavioral telemetry rather than file scans:
- Inspect active scheduled tasks:
Get-ScheduledTask | Where-Object {$_.Actions.Execute -match "powershell|wscript|calc"} - Detect anomalous PowerShell network connections:
Get-NetTCPConnection | Where-Object {$_.OwningProcess -in (Get-Process powershell).Id} - Audit running calc.exe processes with external network sockets:
Get-Process calc -ErrorAction SilentlyContinue | Select-Object Id, ProcessName, Path - Search for suspicious script execution in event logs:
Get-WinEvent -FilterHashtable @{LogName='Microsoft-Windows-PowerShell/Operational'; ID=4104} | Select-Object -First 10
Defensive Blueprint: How to Detect Steganographic Malware
Mitigating advanced steganographic loaders requires organizations to enforce strict runtime isolation and script-blocking policies:
- Block Script Attachments at the Email Gateway: Restrict incoming emails containing compressed archives (.zip, .rar, .7z) holding .js, .vbs, or .hta script files.
- Enforce PowerShell Constrained Language Mode: Prevent arbitrary reflective DLL injection by mandating ConstrainedLanguage mode across standard workstations.
- Implement EDR Memory Telemetry: Deploy modern endpoint detection and response tools configured to monitor process injection into legitimate Windows binaries.
- Restrict Outbound Connectivity to Public Archives: Block programmatic command-line downloads originating from PowerShell directed toward generic file-sharing or archiving services.
Frequently Asked Questions (FAQ)
What is Caminho malware LSB steganography?
Caminho malware LSB steganography is an evasive cyberattack technique where threat actors hide encrypted .NET malware assemblies within the least significant bits of image pixels, evading conventional antivirus detection.
Which malware families does the Caminho loader deploy?
The Caminho loader operates as a Loader-as-a-Service platform, commonly delivering REMCOS RAT, XWorm, and Katz Stealer to achieve persistent unauthorized network access and credential theft.
Why do security scanners fail to detect steganographic images?
Steganographic images retain valid image headers and normal visual appearance. Because the malicious code is distributed across pixel color values, static antivirus scanners classify the file as a harmless graphic asset.
How can organizations protect endpoints from Caminho attacks?
Organizations should block script attachments at mail gateways, enable PowerShell Script Block Logging, enforce endpoint memory scanning, and restrict unmonitored script connections to external archive domains.
This threat analysis was authored, fact-checked, and architecturally verified by the CyberUpdates365 Threat Intelligence Desk. All mitigation workflows conform to official cybersecurity standards as of August 2026.